Home Blog Page 12

Does Cloudflare Pro Protect Business Email? What Businesses Need to Know

0

For many businesses, email is just as important as the company website. It is used to communicate with customers, receive enquiries, send quotations, manage orders and coordinate daily operations.

When a business invests in website security, it is reasonable to ask whether that investment also protects its email accounts.

Cloudflare Pro offers website security and performance capabilities, but there is an important distinction between protecting web traffic and securing an email service. Understanding that distinction helps businesses avoid configuration mistakes and choose the right protection for their online operations.

If your company uses a business email address such as [email protected], here is what you need to know about Cloudflare Pro, DNS configuration and email security.

https://tremhost.com/cloudflare/

What Does Cloudflare Pro Actually Protect?

Cloudflare primarily provides services for internet traffic directed through its network, including website traffic routed through its reverse proxy.

Its capabilities can help protect supported web applications, manage certain malicious requests and improve the delivery of eligible website content.

Business email works differently. Messages are typically delivered through email protocols such as SMTP, while users retrieve messages using IMAP or POP3. These services operate independently of the HTTP and HTTPS traffic normally handled by Cloudflare’s website proxy.

Consequently, putting a company’s website behind Cloudflare does not automatically put its email server behind the same protection.

A business can have a protected website and still need separate measures to secure its mailboxes, email server and domain against spam, phishing, account compromise and email delivery problems.

Can Cloudflare Pro Stop Business Email From Being Hacked?

Not by itself.

Cloudflare’s website security features are not a replacement for email account security. They do not automatically prevent someone from stealing an employee’s password, sending a convincing phishing message or accessing a compromised mailbox.

Email security requires controls designed for the email environment.

Businesses should use strong, unique passwords and enable multi-factor authentication where supported. They should also restrict access to mailboxes, maintain updated email software and investigate unusual sign-in activity.

For organisations using hosted business email, the provider’s security controls and account recovery procedures matter too.

Cloudflare can contribute to the security of a company’s website, but email protection must be considered separately.

Why Cloudflare DNS Settings Matter for Email

Although Cloudflare’s website proxy and email services perform different roles, DNS configuration connects them.

A domain may use several DNS record types, each serving a different purpose. A website typically uses A, AAAA or CNAME records, while email routing commonly relies on MX records and supporting DNS entries.

The MX record identifies the mail servers responsible for receiving messages for a domain. If it is incorrect or points to the wrong destination, incoming email may fail even when the website is working perfectly.

When using Cloudflare DNS, mail-related records must be configured appropriately for the actual email provider.

In particular, mail server hostnames should not be mistakenly proxied as ordinary website traffic. Standard SMTP, IMAP and POP3 connections are not automatically supported by Cloudflare’s regular HTTP/HTTPS proxy.

A DNS configuration error can therefore affect email delivery or prevent email clients from connecting to the correct server.

What Happens If You Accidentally Proxy Your Mail Server?

Imagine a business uses mail.example.com as the hostname for its email server.

If that hostname is configured as a proxied DNS record when the email service expects a direct DNS resolution, standard email clients may be unable to connect correctly.

The exact outcome depends on the DNS records, the service architecture and the protocols being used.

The appropriate configuration is generally to keep the mail server’s DNS record DNS-only when it points directly to the email server, following the email provider’s instructions. MX records themselves are DNS records and are not configured with the usual orange-cloud HTTP proxy toggle.

This is why website and email DNS records should be reviewed together whenever a domain is moved to Cloudflare.

Do not change records simply to make the DNS dashboard look consistent. Different records serve different purposes, and an incorrect change can interrupt an otherwise functioning service.

Can Cloudflare Protect Your Email Server From DDoS Attacks?

Cloudflare’s standard website proxy does not automatically proxy ordinary SMTP, IMAP or POP3 traffic.

If a mail server is exposed directly to the internet, protection for its mail protocols depends on the server infrastructure, network controls and services configured specifically for that environment.

Cloudflare offers products and configurations beyond its standard website proxy, but availability and suitability depend on the product and setup involved.

Businesses should therefore avoid assuming that purchasing Cloudflare Pro automatically protects every open port or service on their hosting server.

If email availability is critical, ask your hosting or email provider what network-level protection, abuse prevention and incident response measures are available for the mail service itself.

What About SPF, DKIM and DMARC?

Cloudflare Pro does not eliminate the need for email authentication.

Three important DNS-based mechanisms help receiving mail systems assess whether messages are authorised and properly authenticated.

SPF, or Sender Policy Framework, identifies the servers authorised to send email for a domain.

DKIM, or DomainKeys Identified Mail, uses cryptographic signatures to help receiving systems verify that a message is associated with an authorised signing domain and has not been altered in transit.

DMARC, or Domain-based Message Authentication, Reporting and Conformance, allows a domain owner to publish a policy for handling messages that fail DMARC checks and to receive reports where supported.

These records are configured in DNS, so they can be managed through Cloudflare when Cloudflare is authoritative for the domain. However, the correct values must come from the business’s email provider.

Incorrect SPF, DKIM or DMARC records can interfere with email authentication and deliverability. Configure them carefully and verify that legitimate sending services are included before tightening enforcement policies.

These controls complement mailbox security; they do not replace it.

How to Secure Business Email Alongside Cloudflare Pro

Businesses should treat website security and email security as related but separate responsibilities.

Start by confirming which provider handles your email and which hostnames are used by its mail servers. Review the domain’s MX, SPF, DKIM and DMARC records and make sure they match the provider’s requirements.

Next, secure the actual mailboxes. Use strong passwords, enable multi-factor authentication where possible, remove access for former employees and review forwarding rules that could silently send company messages to an unauthorised address.

Finally, confirm that the website’s Cloudflare configuration does not interfere with mail-related DNS records. If email stops working after a DNS change, investigate the affected records and mail server connectivity before assuming that the problem is caused by the website firewall.

A properly configured website proxy and a properly configured email service should work alongside one another.

Should Your Business Use Cloudflare Pro?

Cloudflare Pro may be worth considering if your business website needs the additional security and performance capabilities available with the plan.

However, if your primary concern is phishing, spam, compromised mailboxes or email deliverability, you should also evaluate dedicated email security measures. A website protection plan alone does not solve those problems.

Tremhost offers a Cloudflare Pro-based security option from $9 per month. You can review the available service details at Tremhost Cloudflare.

For broader assistance with protecting your online infrastructure, explore Tremhost’s managed cybersecurity services.

Before selecting a service, confirm which protections are included and whether your email service requires separate configuration or security products.

Final Thoughts

Cloudflare Pro can strengthen the security of supported website traffic, but business email requires its own protection and correct DNS configuration.

The most important distinction is simple: securing your website does not automatically secure your inboxes.

By configuring email DNS records correctly, implementing strong mailbox security and understanding the limits of the website proxy, businesses can protect both their online presence and their day-to-day communications more effectively.

Explore website security through Tremhost: https://tremhost.com/cloudflare/

Cloudflare Pro Cache Rules: How to Fix Login, Cart and Checkout Problems

0

A website owner enables Cloudflare caching to improve loading speeds. The homepage becomes faster, images load efficiently, and everything initially appears to be working.

Then the complaints begin.

Customers report that their shopping carts are not updating. Members cannot access their dashboards. A user logs in successfully but is redirected back to the login page. Someone edits website content, yet visitors continue seeing an older version.

These problems can have several causes, but incorrect caching is one possibility worth investigating.

Cloudflare Pro provides useful performance capabilities, but understanding what should and should not be cached is essential. A website that delivers personalised information cannot safely treat every page like a static image.

This guide explains how Cloudflare caching works, why common problems occur and how to investigate them without compromising website functionality.

What Does Cloudflare Actually Cache?

Caching involves storing a reusable copy of content so that future requests can be served without repeatedly retrieving the same resource from the origin server.

Cloudflare can cache eligible content at its network edge. This can reduce repeated requests to the hosting server and improve delivery for visitors.

However, Cloudflare does not cache every page automatically.

Under normal default behaviour, Cloudflare primarily caches eligible static resources. HTML pages are not generally cached by default unless a rule or another configuration makes them eligible.

This distinction matters because problems often arise when website owners introduce broad caching rules without understanding the content being served.

For example, an image displayed on a public product page may be suitable for caching. A shopping cart containing a customer’s selected products is different because its contents change according to the individual user.

The Danger of Caching Personalised Pages

Imagine two customers browsing the same online store.

The first customer adds three products to a shopping cart. The second customer visits the website moments later.

If a poorly configured cache serves personalised HTML across user sessions, the second customer could potentially receive information intended for the first.

That is more serious than a performance problem. It can become a privacy and data exposure issue.

Similar risks can affect membership websites, customer portals, booking systems and learning platforms.

The safest approach is to identify pages that contain user-specific information and ensure that they are not cached inappropriately.

For many websites, login pages, account dashboards, checkout pages and authenticated application endpoints require special handling.

Why Cloudflare Can Cause Login Problems

A login process typically depends on session information, cookies and application-level authentication controls.

When a user submits their credentials, the application verifies the request and establishes an authenticated session. Subsequent requests must be associated with that session.

Problems can occur when caching rules interfere with how personalised responses are delivered.

However, caching is not the only possible cause. Firewall challenges, application plugins, incorrect cookie settings and server-side session problems can also interrupt logins.

If users repeatedly return to the login page after authenticating, begin by determining whether the problem occurs only when Cloudflare is involved.

Review the relevant cache settings, examine the affected response headers and check whether a security rule is challenging or blocking an authentication request.

Do not immediately disable every security feature. Identifying the responsible setting allows you to make a narrower, safer correction.

How to Check Whether Cloudflare Is Caching a Page

One useful diagnostic is the CF-Cache-Status response header.

This header can help indicate how Cloudflare handled the requested resource.

For example, HIT generally indicates that a response was served from Cloudflare’s cache. MISS indicates that the resource was not already available in cache for that request, while BYPASS indicates that caching was bypassed.

Other values may appear depending on the circumstances.

You can inspect response headers using browser developer tools or a command-line utility such as curl.

For example:

curl -I https://example.com/account/

Replace the example address with the relevant URL on your website.

Look for CF-Cache-Status, Cache-Control and other relevant response headers.

If an authenticated account page unexpectedly returns a cached response, investigate immediately. Remember that a single response header is only part of the evidence. Test different user states and confirm how the application handles cookies and personalised content.

How to Configure Cache Rules More Safely

Cloudflare Cache Rules allow website administrators to control which requests are eligible for caching and how cached responses are handled.

A practical starting point is to separate public, reusable content from private or frequently changing content.

Static assets such as public images, stylesheets and scripts can often be cached effectively.

Pages containing personalised account information, shopping carts, checkout sessions or private application data usually need different treatment.

For websites with clearly defined private routes, administrators can create rules that bypass caching for the relevant URL paths.

For example, a website may need to bypass caching for paths such as /account/, /cart/, /checkout/ or its authentication endpoints.

These are examples, not universal rules. Actual URL structures vary between applications, and some platforms use query parameters, cookies or API endpoints that require additional consideration.

Cloudflare also supports cache-rule conditions based on request characteristics such as cookies. Such controls can be useful when an application distinguishes authenticated users from anonymous visitors through session cookies.

The important principle is to configure caching around the application’s behaviour rather than copying a generic rule without testing it.

What About WordPress and WooCommerce?

WordPress websites often combine public content with administrative and personalised functionality.

A typical business website may have public pages that are suitable for caching, while its administrator dashboard and login functionality should be handled differently.

WooCommerce adds further complexity because customers interact with shopping carts, checkout pages, account areas and payment workflows.

Before introducing broad HTML caching, website owners should identify the platform’s session cookies, dynamic endpoints and existing caching integrations.

Test the entire shopping process after making changes. A successful homepage load does not prove that checkout works correctly.

For businesses processing online orders, incorrect caching can interfere with customer experience and potentially cause lost sales.

What to Do When Visitors See Old Content

Sometimes caching does not break a login or checkout. Instead, visitors see an outdated version of a page.

This can happen when content changes at the origin but an older cached response remains available.

If you update a product description, publish a correction or change an important announcement, you may need to purge the relevant cached content.

Before purging everything, check whether the affected URL can be purged individually. A targeted purge is often preferable because it avoids unnecessarily removing other useful cached resources.

Also investigate whether the stale content comes from Cloudflare, a WordPress caching plugin, the hosting server or the visitor’s browser. Multiple caching layers can exist on the same website.

Repeatedly purging Cloudflare will not permanently solve a problem caused by incorrect cache rules or application configuration.

Why Firewall Challenges Can Look Like Cache Problems

Not every Cloudflare-related login issue is caused by caching.

A security challenge applied to an authentication endpoint can interrupt the normal request flow. A user may successfully complete a browser challenge but still encounter a failed login or form submission.

When troubleshooting, examine both the caching configuration and the security rules affecting the endpoint.

If a particular challenge is disrupting legitimate authentication, consider narrowing the rule or applying a more suitable control.

Avoid removing protection from an entire website simply because one endpoint requires different handling.

Can Cloudflare Pro Solve Every Website Performance Problem?

No. Cloudflare can improve the delivery of eligible content and help reduce unnecessary origin requests, but it cannot fix every problem within a website’s application or hosting environment.

A slow database, inefficient plugin, overloaded server or poorly written application can remain slow even with appropriate caching.

Cloudflare Pro adds performance and security capabilities beyond the free plan, but a successful configuration still depends on understanding the website.

The goal should not be to cache as much content as possible. It should be to cache the right content without interfering with application functionality or exposing private information.

Getting Cloudflare Pro Configured Through Tremhost

For businesses that want to explore additional Cloudflare security and performance features, Tremhost offers a Cloudflare Pro-based service from $9 per month.

You can review the offering at Tremhost Cloudflare.

Before choosing a provider, confirm which configuration and support services are included. Websites with shopping carts, membership systems, customer dashboards or other dynamic functionality may require more careful implementation than a simple informational website.

Businesses looking for wider website protection can also explore Tremhost’s managed cybersecurity services.

Final Thoughts

Cloudflare caching can be a valuable performance tool, but incorrect rules can create frustrating or potentially serious problems.

The solution is not necessarily to disable caching. It is to understand which content can be safely reused, which pages contain personalised information and how the website handles sessions, cookies and dynamic requests.

For WordPress websites, online stores and web applications, testing is essential. Review response headers, examine cache rules and verify important user journeys before and after making changes.

A carefully configured Cloudflare setup should improve content delivery without compromising the security or functionality of the website.

Explore Cloudflare Pro-based protection through Tremhost: https://tremhost.com/cloudflare/
Cloudflare Pro for Job Portals: Protect Recruitment Websites From Bots and Abuse

0

Online recruitment has changed how employers find talent and how job seekers discover opportunities. A recruitment website can publish hundreds of vacancies, collect applications, connect employers with candidates and generate revenue through listings or subscriptions.

However, operating a job portal comes with challenges that are easy to overlook. Automated bots can submit spam through application forms, malicious requests can target vulnerable website components, and sudden traffic increases can place additional pressure on the hosting environment.

These problems can affect more than website performance. They can waste recruiters’ time, frustrate applicants and undermine confidence in the platform.

Cloudflare Pro is one option recruitment businesses can consider when strengthening their website security and traffic management. Understanding how its features fit into a wider security strategy helps portal operators decide whether upgrading is worthwhile.

https://tremhost.com/cloudflare/

Why Job Portals Attract Unwanted Traffic

Recruitment websites often expose several interactive features to the public. These may include registration forms, job submission pages, employer dashboards, candidate profiles and application forms.

Public-facing forms can attract automated submissions, while login pages and other application endpoints may be probed for weaknesses. Some bots collect publicly available information, while others generate spam or attempt to misuse website functionality.

Not every automated request is malicious. Search engine crawlers need to discover job listings, and legitimate integrations may access published vacancies. The challenge is distinguishing useful automated activity from traffic that creates risk or unnecessary costs.

A website operator should therefore avoid blocking all bots indiscriminately. Instead, the objective is to reduce harmful activity while allowing legitimate visitors, applicants and search engines to use the platform.

How Cloudflare Pro Can Help Protect a Recruitment Website

Cloudflare operates as a reverse proxy for websites using its proxied DNS records. This allows supported traffic to pass through Cloudflare before reaching the origin server.

Cloudflare Pro includes additional security capabilities beyond the free plan, including web application firewall features. Depending on the applicable plan and configuration, these controls can help identify and block requests matching recognised attack patterns.

For a recruitment portal, that can provide an additional layer of defence for publicly accessible web applications. Security rules may help address certain common attempts to exploit application vulnerabilities before those requests reach the origin server.

However, a WAF cannot replace secure application development, software updates or proper access controls. The recruitment platform itself must still handle user input safely, protect candidate accounts and manage sensitive information responsibly.

Reducing Spam in Job Applications and Contact Forms

Spam can become a serious operational problem when a recruitment website allows anyone to submit applications, post vacancies or contact employers.

A high volume of irrelevant submissions can consume staff time and make genuine applications harder to identify. It can also increase the processing load on the website.

Cloudflare’s available security and traffic-management controls may help address some suspicious requests, depending on the configuration and nature of the activity. However, a firewall alone will not eliminate every type of form spam.

Recruitment platforms should consider complementary measures such as server-side validation, rate limiting where appropriate, form abuse controls and sensible restrictions on repeated submissions. CAPTCHA or other verification mechanisms may also be useful in situations where automated abuse is significant.

The right approach depends on the portal’s design and the behaviour being observed. Security measures should be tested carefully so that legitimate applicants are not unnecessarily prevented from submitting their applications.

Keeping Job Listings Accessible During Traffic Spikes

A popular vacancy can attract substantial attention, particularly when it is shared across social media or promoted by a large employer.

If many people visit the same listing at once, the recruitment platform must deliver pages quickly while continuing to process applications and account activity.

Cloudflare’s caching and content delivery capabilities can help serve suitable content without sending every request to the origin server. Static assets and eligible public pages may benefit, depending on the caching rules and how the application handles dynamic content.

Not every page should be cached in the same way. Candidate dashboards, authenticated employer areas and application workflows may contain personalised information or require fresh data. Incorrect caching can cause functionality problems or expose information that should remain private.

Portal operators should distinguish public job listings from private account pages, configure caching accordingly and test important user journeys after making changes.

Protecting Employer and Candidate Accounts

A recruitment website may hold names, contact details, employment histories, CVs and other personal information. Protecting that information requires more than filtering incoming web traffic.

Cloudflare’s edge protection can complement a wider security strategy, but it does not automatically secure every account, database or application component.

Recruitment businesses should use strong authentication, restrict administrative privileges, keep software and plugins updated, and protect sensitive information through appropriate application and database controls. They should also maintain dependable backups and have a plan for responding to security incidents.

Where possible, origin server access should be restricted so that attackers cannot simply bypass Cloudflare and connect directly to the website’s hosting environment.

These precautions are particularly important for recruitment businesses that process large volumes of applications or provide paid services to employers.

Does Every Recruitment Website Need Cloudflare Pro?

Not necessarily. A small recruitment website with a limited number of listings and modest traffic may find that Cloudflare Free provides a suitable starting point.

A larger job board or recruitment platform may have stronger reasons to evaluate Pro, particularly if it depends on interactive applications, receives persistent suspicious traffic or requires additional web application security features.

The decision should be based on actual needs. Review the features currently included in each plan, identify the problems you need to solve and determine whether the additional capabilities justify the cost.

Remember that a paid security plan does not automatically resolve vulnerabilities in the recruitment software or guarantee uninterrupted service. Hosting capacity, application quality, configuration and ongoing maintenance remain important.

Exploring Cloudflare Pro Through Tremhost

Recruitment businesses looking for additional website security options can explore Tremhost’s Cloudflare offering.

Tremhost offers a Cloudflare Pro-based security option from $9 per month. You can review the service details, available options and applicable terms on the Tremhost Cloudflare page.

Before choosing a provider, confirm which features are included, how the service is configured and what technical support is available. These details help you determine whether the offering fits your recruitment platform’s requirements.

For businesses seeking broader website protection, Tremhost’s managed cybersecurity services are another option to explore.

Final Thoughts

Job portals need to balance accessibility with security. Applicants must be able to discover vacancies and submit applications, while employers need a dependable platform for managing recruitment activities.

Cloudflare Pro may help recruitment businesses strengthen their edge security and manage supported website traffic, but it works best as part of a broader strategy that includes secure application development, account protection, software maintenance and reliable backups.

By identifying the portal’s main risks and configuring the appropriate controls, recruitment businesses can make more informed decisions about protecting their websites and supporting a better experience for candidates and employers.

Explore Cloudflare security through Tremhost: https://tremhost.com/cloudflare/

Cloudflare Pro for News Websites: Protect Your Content and Keep Readers Connected

0

For a news website, traffic can change dramatically within minutes. An ordinary news report might attract a steady stream of readers, while a major announcement, breaking story or viral investigation can bring thousands of visitors to the same page at once.

That attention is valuable, but it also creates technical challenges. If a website becomes slow or unavailable when readers need it most, publishers risk losing traffic, advertising opportunities and audience trust.

At the same time, news websites face the same online threats as other public-facing platforms. Automated bots, malicious requests and attempts to exploit application vulnerabilities can put pressure on websites that already need to deliver content quickly and reliably.

This is where Cloudflare Pro becomes worth considering. By combining Cloudflare’s network capabilities with additional security and performance features, publishers can explore ways to improve their websites’ resilience while delivering content to readers.

https://tremhost.com/cloudflare/

Why News Websites Need More Than Reliable Hosting

Reliable hosting is essential for every news website, but hosting alone does not address every challenge associated with delivering content online.

A publisher might have a well-maintained server and still experience problems when traffic rises sharply. Repeated requests can consume resources, while poorly optimised images, inefficient application code and database bottlenecks can make important articles slow to load.

Security is another consideration. News websites often contain public comment sections, contact forms, user accounts or content management systems that require ongoing maintenance. These features can introduce opportunities for spam, automated abuse and attempts to exploit software vulnerabilities.

A layered approach can help address these challenges. Hosting provides the environment where the website operates, while Cloudflare can handle supported traffic at the network edge before requests reach the origin server.

Cloudflare Pro adds capabilities beyond the free plan that may be useful to publishers, depending on their requirements and configuration.

How Cloudflare Pro Can Help During Breaking News

Imagine a news organisation publishing an important story that suddenly attracts readers from across the country and abroad. Links are shared on social media, other publications reference the report, and visitors begin opening the same article simultaneously.

A website that is not prepared for this increase may become slow or temporarily unavailable.

Cloudflare’s network can help deliver eligible cached content without requiring every request to be served directly by the origin server. This can reduce the amount of work performed by the hosting environment when caching is configured appropriately.

However, caching is not automatic protection against every traffic spike. Dynamic pages, personalised content and requests that cannot be served from cache may still require processing by the origin server. Publishers should therefore review caching behaviour, hosting capacity and application performance together.

For news organisations covering unpredictable events, preparing these settings before a major story breaks is much more useful than attempting to optimise the website after readers begin experiencing problems.

Protecting News Websites Against Common Web Attacks

News websites depend on content management systems, plugins, databases and other software components. If these systems contain weaknesses, attackers may attempt to exploit them through malicious web requests.

Cloudflare Pro includes web application firewall capabilities that can help detect and block requests matching applicable security rules. These controls can provide an additional layer of defence against certain common web application attacks.

For a publisher, this matters because a compromised website can damage credibility, interrupt publication and potentially expose information held by the application.

Nevertheless, a firewall should not be treated as a replacement for software updates, strong administrator passwords, multi-factor authentication where available, secure hosting and reliable backups. If a vulnerability exists in the website itself, the underlying software still needs to be fixed.

Publishers should also review security events and test their websites after making configuration changes. An overly aggressive rule can interfere with legitimate visitors, editorial workflows or content management functions.

Managing Bots Without Blocking Real Readers

Not all automated traffic is harmful. Search engines need to crawl articles, monitoring systems check availability, and other legitimate services may retrieve publicly available content.

At the same time, some bots repeatedly request pages, submit spam or probe websites for vulnerabilities. Unwanted automated activity can consume resources and complicate the task of distinguishing normal audience behaviour from suspicious requests.

Cloudflare provides traffic-management and security controls that can help website operators handle certain types of unwanted activity. The appropriate configuration depends on the traffic involved, the available plan features and the publisher’s technical requirements.

News organisations should avoid blocking automated traffic indiscriminately. Search engine accessibility, legitimate integrations and important editorial tools must continue to function properly.

The objective is to reduce harmful activity without creating unnecessary barriers for genuine readers.

Does Cloudflare Pro Make News Websites Faster?

Cloudflare Pro offers performance features that may improve the delivery of suitable website content. The actual improvement depends on the site’s configuration, the location of its readers, its caching strategy and the performance of the origin server.

For a publication containing large photographs, embedded media and frequently updated articles, image optimisation and appropriate caching may be particularly relevant.

However, Cloudflare cannot independently solve every performance problem. A website with inefficient database queries, excessive JavaScript, oversized page layouts or an overloaded hosting environment may remain slow even when traffic passes through Cloudflare.

Publishers should measure their existing performance, identify the main bottlenecks and then test the effect of individual improvements. This approach helps establish whether the changes are producing meaningful results rather than assuming that a subscription automatically makes every page faster.

Cloudflare Pro and the Protection of Editorial Websites

A news website is more than a collection of articles. It may include editorial dashboards, journalist accounts, publishing tools, advertising integrations and subscriber services.

These components require appropriate access controls and ongoing maintenance. Cloudflare’s edge security can complement a wider security strategy, but publishers must still protect administrative accounts and restrict access to sensitive systems.

It is also important to consider the origin server. If visitors can connect directly to the server and bypass Cloudflare, some of the protection provided by the proxy may be undermined. Where practical, publishers should restrict origin access to trusted traffic and review the exposure of other services.

Security planning should include backups and a tested recovery process. If a website is compromised or an important component fails, the ability to restore a clean, working version can be just as important as preventing the initial incident.

Is Cloudflare Pro Worth Considering for Publishers?

The answer depends on the publication’s size, technical setup, traffic patterns and security requirements.

A small local publication with modest traffic may find that Cloudflare Free provides an adequate starting point. A larger publisher, or one whose website plays a critical role in advertising revenue and audience engagement, may have reasons to evaluate the additional capabilities offered by Pro.

The decision should be based on specific needs rather than the assumption that every website must use a paid plan. Publishers should compare the currently available features, understand the limitations and determine whether the additional controls justify the cost.

For organisations that want help exploring their options, Tremhost offers a Cloudflare Pro-based security option from $9 per month. You can review the available service details at Tremhost Cloudflare.

Businesses seeking a broader approach to protecting their websites can also explore Tremhost’s managed cybersecurity services.

Before choosing a service, publishers should confirm what is included, how the configuration is managed and what technical assistance is available.

Final Thoughts

News websites operate in an environment where traffic can change quickly and website availability directly affects the reader experience. Preparing for traffic surges, maintaining application security and delivering content efficiently are all important parts of running a reliable publication.

Cloudflare Pro can contribute to this effort through additional security and performance capabilities, but its effectiveness depends on appropriate configuration and the quality of the wider hosting and application environment.

For publishers evaluating their options, the best starting point is to identify their main risks, measure existing performance and choose tools that address genuine operational needs.

Explore Cloudflare protection through Tremhost: https://tremhost.com/cloudflare/
Cloudflare Pro vs Free: Which Plan Is Better for Your Website?

0

Cloudflare is widely used by website owners who want to improve performance, manage traffic and strengthen website security. One of its biggest advantages is that businesses can begin with a free plan and consider upgrading as their requirements grow.

However, choosing between Cloudflare Free and Cloudflare Pro is not always straightforward. A personal blog with limited traffic may have very different requirements from an online store, a professional services company or a website that generates customer enquiries every day.

The question is not simply whether Cloudflare Pro is better than Free. It is whether the additional features available with Pro are relevant to your website, your customers and the risks your business faces.

Understanding the differences can help you make an informed decision before spending money on website protection.

https://tremhost.com/cloudflare/

What Is Cloudflare Free?

Cloudflare Free provides website owners with access to important performance and security capabilities. These can include content delivery network services, DDoS protection, SSL/TLS support, DNS management and access to selected security controls.

By routing supported website traffic through Cloudflare’s network, website owners can benefit from caching, traffic handling and protection against certain types of malicious activity.

For a new website, personal blog or small project, these capabilities can provide a useful starting point. You can improve the delivery of website content and introduce an additional layer of protection without committing to a paid plan.

Free does not mean that the service is useless or insecure. In fact, many websites can operate successfully with Cloudflare Free when it is configured appropriately and supported by good hosting and application security practices.

The limitation is that the free plan does not include every feature available across Cloudflare’s paid plans.

What Does Cloudflare Pro Add?

Cloudflare Pro is designed for website owners who need additional capabilities beyond the free offering. Depending on current plan terms, these may include enhanced web application firewall features, more advanced security controls, image optimisation and additional performance tools.

These features can be valuable when a website plays a direct role in generating revenue, collecting enquiries or delivering services to customers.

For example, an online store may need stronger controls against common web application attacks. A business website may want additional options for managing suspicious requests, while a content-heavy website may benefit from available image optimisation features.

The key is to assess the actual features included in the current plan and determine whether they address a genuine requirement. A paid subscription should solve a problem or provide a useful capability, rather than simply look more impressive on a pricing page.

Cloudflare Pro vs Free: The Main Differences

Website security

Both plans provide security benefits, but the available controls and features differ.

Cloudflare Free offers a useful foundation for many websites. Pro adds access to additional security capabilities, including enhanced web application firewall features, subject to the current plan and configuration.

A WAF evaluates web requests against security rules to help identify and block certain malicious patterns. This can help reduce exposure to common web application attacks, although it does not eliminate every vulnerability.

If your website handles customer information, depends on online enquiries or runs a business-critical application, the additional controls available with Pro may be worth evaluating.

Performance optimisation

Both plans can improve website delivery through Cloudflare’s network. The exact performance benefits depend on the website, the content being delivered, caching behaviour and the origin server.

Pro provides access to additional optimisation features that may benefit eligible websites. Image-heavy sites, for instance, should assess whether the available image optimisation tools suit their content and traffic patterns.

Upgrading alone does not guarantee that a website will load faster. Poor hosting performance, oversized scripts, inefficient database queries and badly configured caching can still cause slowdowns.

Control and configuration

The available security and performance controls differ by plan. Before upgrading, review the current feature comparison and identify which capabilities matter for your website.

A business that only needs basic DNS management and caching may not require every Pro feature. Another business may find that additional firewall rules or optimisation options justify the cost.

The right choice depends on requirements, not assumptions.

Is Cloudflare Free Enough for a Business Website?

Sometimes, yes.

A simple company website that mainly provides contact details, service descriptions and basic information may operate comfortably with Cloudflare Free. If it receives modest traffic and does not require additional paid-plan features, upgrading may not be necessary.

However, the decision should not be based on website size alone. Even a small business website can be important if it generates sales leads, receives customer bookings or supports the company’s reputation.

Consider what would happen if the website were repeatedly targeted by malicious requests, if customers could not access it or if a vulnerable application component were exploited.

These questions help you evaluate the business impact of website security rather than treating the choice as a technical specification exercise.

When Should You Consider Cloudflare Pro?

Cloudflare Pro is worth considering when your website would benefit from features that are not available or are more limited under the free plan.

An online store may want additional web application security controls. A professional services company may want stronger protection for a website that generates valuable enquiries. A publisher may want to evaluate additional performance tools for its content.

A business should also consider the time and expertise required to configure and maintain its security settings. Buying a plan does not automatically mean every available feature is enabled or optimally configured.

Before upgrading, identify the problem you want to solve, confirm that Pro includes a relevant feature and test the configuration after making changes.

How Much Does Cloudflare Pro Cost?

Cloudflare’s direct pricing and plan terms can change, so always check the current official pricing before making a purchase decision.

Businesses can also explore provider-based options. Tremhost offers a Cloudflare Pro-based security option from $9 per month, giving eligible customers another route to consider.

You can review the service details at Tremhost Cloudflare.

When comparing prices, make sure you understand what each option includes. Confirm whether the service covers configuration, technical assistance, ongoing management or other services, and compare those terms with what you would receive by subscribing directly.

The lowest advertised price is useful only when the product and service match your requirements.

Does Cloudflare Pro Replace Website Hosting Security?

No. Cloudflare and your hosting environment perform different roles.

Cloudflare can filter and manage traffic passing through its network, but your hosting account and application still need appropriate security controls. Outdated software, weak passwords, compromised administrator accounts and exposed origin services can create risks that a WAF alone cannot resolve.

For WordPress websites, maintain core software, themes and plugins. Use strong authentication, keep dependable backups and restrict access to administrative tools. Where practical, configure the origin server so that visitors cannot simply bypass Cloudflare and connect directly to it.

A layered security approach helps ensure that your website is not relying on one product to address every possible threat.

How to Choose the Right Cloudflare Plan

Start with the website’s purpose. If it is a personal project or a basic informational website, Free may provide everything you currently need.

If the website is important to your business, examine the additional features in Pro and decide whether they address meaningful security or performance requirements. Review the current official plan documentation rather than relying on outdated comparisons.

Finally, consider who will configure the service and investigate issues when something goes wrong. A security product is most useful when it is implemented correctly and supported by sound website maintenance practices.

Businesses seeking a broader security approach can also explore Tremhost’s managed cybersecurity services.

Final Verdict: Cloudflare Pro or Free?

Cloudflare Free is a strong starting point for many websites. It offers useful security and performance capabilities without a paid subscription.

Cloudflare Pro is worth considering when its additional features address specific needs, particularly for websites that play an important role in customer acquisition, online sales or business operations.

The best plan is the one that fits your requirements, not necessarily the most expensive one.

If you are comparing Cloudflare Pro options for your business, review the current features, understand what the service includes and choose a configuration that supports your website’s security and performance goals.

Explore your options with Tremhost: https://tremhost.com/cloudflare/
Cloudflare Pro WAF Explained: How It Helps Protect Your Website

0

A website can look perfectly normal to its visitors while receiving requests designed to exploit vulnerabilities, access sensitive information or disrupt its operation. These threats are not always obvious. Some attacks arrive through automated bots, while others target weaknesses in the applications and software that power a website.

This is where a web application firewall becomes important.

Cloudflare Pro includes web application firewall capabilities designed to help protect websites against common web-based threats. For businesses that depend on their websites to attract customers, process enquiries or provide online services, understanding how this protection works can help them make better security decisions.

But what exactly does the Cloudflare Pro WAF do? How does it work, and is it enough to secure an entire website?

https://tremhost.com/cloudflare/

What Is a Web Application Firewall?

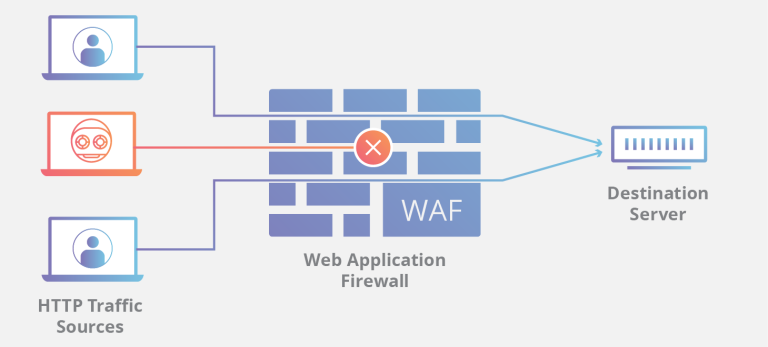
A web application firewall, commonly known as a WAF, examines HTTP and HTTPS requests travelling to a website and applies security rules to identify potentially malicious traffic.

Think of it as a security checkpoint between visitors and your website. Legitimate requests should reach the website, while requests matching configured security rules can be blocked, challenged or otherwise handled according to the firewall’s settings.

A traditional network firewall and a web application firewall do not perform exactly the same job. A network firewall focuses on network traffic and connections, while a WAF concentrates on requests made to web applications.

That distinction matters because many website attacks use the same protocols as ordinary visitors. A malicious request can arrive over HTTPS and still attempt to exploit an application vulnerability. Encryption protects data in transit, but it does not automatically make every request trustworthy.

How Cloudflare Pro WAF Helps Protect Websites

Cloudflare operates as a reverse proxy for websites using its proxied DNS records. When configured correctly, requests pass through Cloudflare’s network before reaching the origin server.

This positioning allows Cloudflare to apply security controls to web traffic before it reaches the website’s hosting environment.

Cloudflare Pro provides access to additional application security features, including its web application firewall capabilities. Depending on the applicable plan, configuration and available rulesets, these controls can help identify and block requests associated with common attack patterns.

For example, a malicious request might attempt to manipulate a database query, exploit a vulnerable application endpoint or submit suspicious input to a web form. Relevant firewall rules can inspect request characteristics and take action when a request matches a rule.

The important point is that a WAF helps reduce exposure to common web threats. It is not a guarantee that every attack will be detected or that every vulnerability will be prevented from being exploited.

What Types of Attacks Can a WAF Help Address?

SQL injection attempts

SQL injection occurs when an attacker attempts to manipulate a database query through application input. If an application handles that input incorrectly, the attacker may be able to access or manipulate data.

WAF rules can detect patterns associated with common SQL injection attempts and block matching requests. However, application developers must still use parameterised queries, validate input appropriately and follow secure coding practices.

Cross-site scripting attempts

Cross-site scripting, often abbreviated as XSS, involves injecting malicious scripts into content that is later processed by a victim’s browser.

Depending on the attack and applicable rules, a WAF can help detect suspicious requests associated with common XSS patterns. It should complement, rather than replace, output encoding, input handling and other application-level security controls.

Suspicious automated traffic

Not every bot is malicious. Search engine crawlers, monitoring services and other automated tools can serve legitimate purposes. However, some automated traffic is designed to probe websites, submit spam or repeatedly target application endpoints.

Firewall rules and related traffic controls can help businesses manage suspicious requests. The correct approach depends on the traffic pattern, the website’s requirements and the security features available under the selected plan.

Attempts to exploit known vulnerabilities

Attackers frequently scan websites for weaknesses in content management systems, plugins and other application components. WAF rules can help block requests associated with recognised attack techniques.

Nevertheless, a firewall cannot reliably compensate for every outdated plugin, compromised administrator account or unknown vulnerability. Software updates and secure access controls remain essential.

Why Cloudflare Pro WAF Configuration Matters

Activating a security product is only one part of protecting a website. The rules that are enabled, the way traffic is routed and the handling of legitimate requests all influence the final result.

A poorly configured firewall may block genuine customers, interfere with application functionality or leave important security gaps.

Businesses should review the security rules available to their plan, understand what actions those rules take and monitor the resulting security events. When a legitimate request is blocked, the appropriate response is to investigate the rule and request rather than disabling protection indiscriminately.

For websites that depend on online payments, customer portals, booking systems or enquiry forms, testing critical functions after security changes is particularly important.

Cloudflare’s security controls should be configured around the website’s actual needs, not simply enabled without review.

Is Cloudflare Pro WAF Enough to Secure a Website?

Cloudflare Pro can strengthen a website’s security, but no single service eliminates every risk.

A WAF primarily evaluates web requests passing through the configured Cloudflare proxy. It does not automatically fix vulnerable website code, remove malware already installed on a server, prevent every account takeover or secure every service running on the origin server.

The hosting environment matters, too. If an attacker can connect directly to an origin server and bypass Cloudflare, some of the protection offered by the proxy may be undermined. Origin access should therefore be reviewed and restricted where practical.

A complete security approach should combine Cloudflare’s edge protection with regular software updates, strong administrator authentication, reliable backups, appropriate server security and a recovery plan.

For WordPress websites, for example, keeping themes and plugins updated is just as important as managing traffic at the network edge.

Cloudflare Pro Directly or Through a Provider?

Businesses can evaluate Cloudflare plans directly or explore service providers that offer a Cloudflare Pro-based service with additional setup and support.

The right option depends on what the business needs. Some organisations are comfortable managing DNS, security settings and troubleshooting themselves. Others prefer assistance with configuration and ongoing technical issues.

Tremhost offers a Cloudflare Pro-based security option from $9 per month. Businesses can review the service and its applicable features on the Tremhost Cloudflare page.

Before choosing any provider, confirm exactly what is included, how the service is provisioned, who manages the configuration and what support is available. A provider’s price should be assessed alongside the actual service delivered, not treated as a substitute for understanding the plan.

Businesses looking for broader assistance can also explore Tremhost’s managed cybersecurity services.

How to Get More Value From Cloudflare Pro WAF

Start by confirming that the website’s DNS records are configured correctly and that the relevant records are proxied through Cloudflare. Review the security features available under your plan and understand which rulesets and controls are active.

Next, inspect security events to identify blocked requests and recurring patterns. Test important website functions, including forms, login pages and customer-facing applications, after making changes. Finally, make sure the origin server is not unnecessarily exposed and that the website’s software and administrator accounts are maintained securely.

These steps help turn a security subscription into a more deliberate protection strategy.

Final Thoughts

Cloudflare Pro WAF is a useful layer of defence for businesses that want to reduce exposure to common web application attacks. Its value comes from inspecting requests at the edge and applying security rules before suspicious traffic reaches the origin server.

However, effective website security requires more than a firewall. Correct configuration, secure application code, patched software, protected origin infrastructure and dependable backups all contribute to a stronger defence.

If you are considering Cloudflare Pro for your business website, explore the features available to your plan, understand the limitations and choose a setup that fits your actual security requirements.

Explore Cloudflare security through Tremhost: https://tremhost.com/cloudflare/

Cloudflare Pro for Small Businesses: Is It the Right Choice?

0

For a small business, a website can be one of its most valuable commercial assets. It introduces the company to potential customers, generates enquiries, showcases products and services, and gives people a way to contact the business outside normal working hours. Yet many small businesses invest in building their websites without giving the same attention to protecting them.

The challenge is understandable. Business owners have to balance hosting, software, advertising, staffing and other operating costs. Cybersecurity can seem complicated, especially when providers use technical terms that are difficult to translate into practical business benefits.

Cloudflare Pro is one option worth understanding. It provides additional website security and performance capabilities beyond Cloudflare’s Free plan. For businesses that depend on their online presence, those capabilities may help strengthen the protection surrounding their public-facing websites.

But is Cloudflare Pro necessary for every small business? What does it actually provide, and how can a business decide whether the additional cost is justified?

Through Tremhost, businesses can explore Cloudflare Pro-based website protection from $9 per month. Understanding the features, limitations and available purchasing options can help you decide whether it is the right fit for your website.

https://tremhost.com/cloudflare/
Why Small Businesses Should Take Website Protection Seriously

A common misconception is that cyberattacks primarily target large corporations. In reality, automated systems can scan websites across the internet without an attacker having to select each business individually.

A small company website may run outdated software, use a vulnerable plugin or expose an application that has not been properly maintained. Automated scanners can discover these weaknesses and generate requests intended to identify exploitable systems.

The consequences depend on the website and the weakness involved. A compromised site might display unauthorised content, redirect visitors or become a platform for distributing malicious material. Unwanted traffic may also contribute to performance problems, while certain attacks can disrupt access to the website.

For a small business, these problems can affect customer confidence and operations. A company that relies on online enquiries may miss opportunities when its website becomes unavailable. A retailer may experience disruption to its customer journey. A professional services firm may need to spend valuable time recovering its online presence.

None of this means every business needs an expensive enterprise security package. It means that website protection should be proportionate to the importance of the website, the risks it faces and the resources available to maintain it.

What Is Cloudflare Pro?

Cloudflare Pro is a paid service level designed for websites that need additional security and performance capabilities beyond those available in the Free plan.

Cloudflare can sit between website visitors and the server hosting the website when the relevant DNS records are configured and proxied correctly. Supported requests pass through Cloudflare’s network before reaching the origin server, allowing available traffic-management and security controls to be applied.

One important capability is the web application firewall, commonly called a WAF. A WAF evaluates web requests against security rules designed to identify and block certain malicious activity. Cloudflare Pro includes additional WAF capabilities that may help businesses protect supported web applications against particular web-based threats.

Cloudflare also provides DDoS protection for supported traffic. Distributed denial-of-service attacks attempt to overwhelm an online service with traffic or requests from multiple sources. Protection at the network layer can help mitigate supported attacks, although it cannot guarantee uninterrupted service in every circumstance.

Performance is another consideration. Cloudflare can cache eligible content and deliver it through its distributed network. Depending on the website’s configuration, this may improve the delivery of static resources and reduce repeated requests to the origin server.

These features make Cloudflare Pro worth evaluating for businesses that depend on their websites. However, its value depends on whether the additional capabilities address the business’s actual requirements.

Cloudflare Free vs Cloudflare Pro: Does Your Business Need to Upgrade?

Cloudflare’s Free plan already provides useful foundational services, including CDN functionality and DDoS protection. A small informational website with limited functionality may find that these capabilities are sufficient for its current needs.

Cloudflare Pro adds plan-specific features, including additional web application firewall capabilities and other security and performance options. These may be useful for a business that needs more control over how supported web traffic is handled.

Consider a company website that generates enquiries every day. Its owners may want additional application security controls because the website plays an important role in attracting customers. An online retailer may have different requirements because it needs to maintain a reliable shopping experience and protect its public-facing application.

In either case, the decision should be based on the website’s requirements rather than the assumption that a paid subscription automatically makes every website secure.

A business should review the features available under each plan, identify the risks it needs to address and determine whether the additional capabilities justify the cost. If the Free plan already meets its needs, upgrading may not be necessary.

The objective is to choose the appropriate level of protection, not simply the most expensive option available.

How Much Does Cloudflare Pro Cost?

Price is an important consideration for small businesses, particularly when comparing direct subscriptions with services offered through technology providers.

Cloudflare Pro is commonly associated with a standard direct price of $25 per month for a website on monthly billing. However, businesses can also explore alternative purchasing arrangements through providers offering Cloudflare-based services.

Tremhost offers Cloudflare Pro-based protection from $9 per month, with an advertised annual option of $90 per year.

At $9 per month, twelve monthly payments total $108. The $90 annual option therefore saves $18 compared with paying monthly for a full year.

The difference provides small businesses with another option when budgeting for website protection. However, price should not be the only consideration. Businesses should verify which features are included, how many websites are covered and what setup or support arrangements apply.

The advertised Tremhost price is for its Cloudflare Pro-based offering and should not be confused with Cloudflare’s standard direct subscription price. Before purchasing, review the service terms and confirm that the offering matches your requirements.

You can explore the available options on Tremhost’s Cloudflare services page.

What Cloudflare Pro Can and Cannot Protect

Understanding the limitations of Cloudflare Pro is essential when deciding whether it suits your business.

When correctly configured, Cloudflare can help manage supported web traffic, provide additional web application firewall capabilities and mitigate certain DDoS attacks. It can also help deliver eligible content more efficiently.

However, it does not automatically update your website’s software, repair insecure code, remove existing malware or prevent every account compromise. If your WordPress installation contains a vulnerable plugin, that vulnerability still needs to be addressed.

The hosting environment also matters. If the origin server is directly accessible and accepts web traffic that bypasses the intended Cloudflare protection layer, additional network restrictions may be appropriate. These must be configured carefully to avoid disrupting legitimate services.

Businesses should continue maintaining reliable backups, updating software, using strong administrator credentials and enabling multi-factor authentication where available.

If a website has already been compromised, activating Cloudflare is not a substitute for investigating the incident, removing malicious content and restoring a trustworthy environment.

Cloudflare Pro is best understood as one layer in a wider website security strategy.

Is Cloudflare Pro Worth It for a Small Business?

The answer depends on what your website does for your business.

If the website is a simple informational page and the Free plan meets your requirements, paying for Pro may offer limited additional value. If your website generates leads, supports customer interactions or contributes directly to revenue, additional security and performance capabilities may deserve closer consideration.

The potential cost of a website incident also matters. A business may need to account for recovery work, lost enquiries, interrupted operations and the time spent resolving technical problems. These costs vary significantly, and no security subscription can eliminate them all.

Cloudflare Pro may be a sensible option when its additional features address identifiable risks and fit the website’s technical environment. Businesses should evaluate the plan against their needs rather than purchasing it solely because it is marketed as a premium service.

For small businesses without dedicated technical staff, the purchasing and support arrangements are also worth considering. A provider that understands website infrastructure may help make the service easier to deploy and maintain, provided the scope of that assistance is clearly defined.

Why Consider Cloudflare Pro Through Tremhost?

Tremhost provides Cloudflare Pro-based website protection from $9 per month, giving businesses an alternative way to explore Cloudflare’s additional capabilities.

The offering is particularly relevant to organisations that want to compare pricing and evaluate the convenience of working with a technology provider alongside their website infrastructure.

Before signing up, establish exactly what is included in the selected service. Confirm the number of websites covered, which Cloudflare features are available, whether initial configuration is included and what support is provided if a problem occurs.

These questions matter because buying access to a security platform and having a website correctly configured are not necessarily the same thing.

Visit Tremhost’s Cloudflare services page to review the offering. If your business requires assistance beyond public-facing website protection, you can also explore Tremhost’s managed cybersecurity services.

How to Decide Whether Cloudflare Pro Is Right for You

Start by identifying the role your website plays in the business. Consider whether it generates enquiries, supports sales, provides customer services or simply publishes basic information.

Next, review your current security arrangements. Check that your website software is updated, backups are reliable, administrator access is controlled and the hosting environment is appropriately maintained.

Then compare your requirements with Cloudflare’s Free and Pro features. If Pro provides additional capabilities that address your risks, evaluate the available purchasing options and confirm what support is included.

Finally, remember that security is an ongoing responsibility. Whichever plan you choose, continue monitoring your website, maintaining your software and investigating unusual behaviour.

Cloudflare Pro can be a useful addition when its features match your business requirements. It is not a guarantee against every threat, and it does not replace good website maintenance.

For businesses considering an affordable Cloudflare Pro-based option, Tremhost offers protection from $9 per month. Visit Tremhost’s Cloudflare services page to learn more and decide whether it is suitable for your website.

Your business website deserves protection that reflects its importance. The right choice begins with understanding what you need, what the service provides and how the two fit together.

Cloudflare Pro for SaaS Businesses: Protect Customer Portals and Web Applications

0

For a software-as-a-service business, the website is often much more than a marketing channel. Customers may depend on it to access their accounts, manage subscriptions, use business tools, view reports or interact with services that support their daily operations. When these applications become unavailable or experience security problems, the impact can extend beyond lost website visits.

A SaaS company might operate a customer dashboard, a subscription management portal, an online booking platform or a web application used by businesses across multiple locations. Each application has its own technical requirements, but all depend on a reliable and appropriately secured online environment.

As these businesses grow, they must consider more than application development. They also need to think about unwanted traffic, vulnerable endpoints, automated requests and attempts to exploit weaknesses in their web applications.

Cloudflare Pro offers additional website security and performance capabilities that may help protect suitable public-facing applications. Through Tremhost, businesses can explore Cloudflare Pro-based protection from $9 per month.

The important question is not whether every SaaS company needs the same security plan. It is whether the available features match the application’s architecture, exposure and security requirements.

Why SaaS Businesses Need to Think Beyond Website Hosting

A traditional company website might primarily display information about products and services. A SaaS application, by contrast, may handle authenticated sessions, customer records, account settings and requests that trigger complex operations on the server.

This creates a different set of considerations. A customer portal might need to process frequent requests while maintaining strict access controls. A reporting application may perform expensive database queries. A subscription platform may rely on third-party services for billing, authentication or notifications.

If the application is poorly maintained, attackers may attempt to exploit vulnerabilities in its software or configuration. Excessive requests can also consume resources, particularly when they trigger resource-intensive operations.

These risks do not mean that every SaaS application is under active attack. They highlight the importance of understanding how the application works, which components are exposed to the internet and what protections are appropriate.

Reliable hosting, secure development practices, appropriate authentication and ongoing maintenance remain essential. A traffic-management and security layer can complement these measures, but it cannot replace them.

How Cloudflare Pro Can Help Protect Public-Facing Applications

Cloudflare can operate between website visitors and an origin server when the relevant DNS records are configured and proxied correctly. This allows supported HTTP traffic to pass through Cloudflare’s network before reaching the application infrastructure.

Cloudflare Pro includes additional web application firewall capabilities that can help identify and block certain malicious HTTP requests. Depending on the available rules and configuration, these protections may help reduce exposure to particular web-based attacks.

Cloudflare also provides DDoS protection for supported traffic. Distributed denial-of-service attacks attempt to overwhelm an online service with traffic or requests from multiple sources. Protection at the network layer can help mitigate supported attacks, although it cannot guarantee uninterrupted availability under every circumstance.

For SaaS businesses, these capabilities may be useful for public-facing websites, customer portals and other compatible web applications. However, the exact benefits depend on the application’s design and the traffic being protected.

Businesses should verify which hostnames and services are actually covered. Protecting a public marketing website does not automatically mean that every API, subdomain, remote service or backend system receives the same protection.

Protecting Customer Portals Without Disrupting Legitimate Users

Customer portals must distinguish legitimate requests from suspicious activity while remaining convenient to use. Overly aggressive security settings can interfere with normal customer behaviour, while insufficient controls may leave unnecessary exposure.

For example, a customer dashboard may generate repeated requests as users navigate between pages. An API may receive automated requests from an authorised application. A security rule that does not account for these behaviours could block legitimate traffic.

Before introducing or modifying firewall rules, SaaS operators should understand their application’s normal request patterns. They should test login workflows, account management, API calls and other important functions after configuration changes.

Authentication and authorisation also remain critical. Cloudflare Pro does not automatically ensure that every customer can access only their own records. Those controls must be correctly implemented within the application and its supporting infrastructure.

Similarly, a web application firewall cannot guarantee that business logic is free from vulnerabilities. Developers must still validate inputs, enforce permissions, manage sessions securely and test their applications appropriately.

The objective is to combine suitable traffic protection with secure application design rather than rely on one layer to solve every problem.

Can Cloudflare Pro Improve Application Performance?

Performance can affect how customers perceive a SaaS product. Slow dashboards, delayed responses and unreliable access can make an application frustrating to use, particularly when customers depend on it for work.

Cloudflare can cache eligible content and deliver it through its distributed network. This may improve the delivery of static resources and reduce repeated requests to the origin server.

However, SaaS applications frequently generate personalised or dynamic responses. Account information, reports, subscription details and customer-specific data generally require careful caching policies. Such content should not be cached indiscriminately, because incorrect configuration could expose information or display outdated results.

Cloudflare also cannot independently fix every performance bottleneck. Slow database queries, inefficient application code, limited server capacity and third-party service failures may require changes within the application or infrastructure.

SaaS operators should measure performance, identify the source of delays and test changes carefully. Cloudflare’s capabilities can contribute to a suitable delivery strategy, but the outcome depends on the complete technical environment.

Why Cloudflare Pro Is Not a Complete SaaS Security Strategy

A common mistake is to assume that placing an application behind Cloudflare automatically makes it secure. In reality, several important responsibilities remain with the SaaS provider.

Application vulnerabilities must be identified and corrected. Administrator accounts require strong authentication. Customer permissions must be enforced correctly. Servers and software need maintenance, and backups must be available if recovery becomes necessary.

The origin infrastructure also deserves attention. If the origin server accepts direct web connections that bypass the intended Cloudflare protection layer, additional restrictions may be required. These controls must be implemented carefully to avoid interrupting legitimate traffic or administrative access.

SaaS businesses should also distinguish public-facing web protection from the security of internal systems, databases, email services and other infrastructure. Those assets may need separate controls based on their exposure and risk.

Cloudflare Pro can contribute an additional layer of protection, but it does not replace secure development, infrastructure hardening, monitoring or incident response.

Is Cloudflare Pro Suitable for Your SaaS Business?

The answer depends on what the business operates and which features it needs.

A startup running a public website alongside a relatively simple web application may have different requirements from a platform serving thousands of customers through multiple APIs and complex backend services.

Cloudflare’s Free plan already provides useful foundational capabilities, including CDN functionality and DDoS protection. Cloudflare Pro adds plan-specific security and performance capabilities, including additional web application firewall features.

SaaS operators should compare the available features with their actual requirements before choosing a plan. They should also verify that the product supports the traffic, hostnames and application behaviour they intend to protect.

Complex applications may require additional security controls, specialised architecture or a more comprehensive assessment. A low monthly price should not be interpreted as proof that every component of a SaaS platform is covered.

Get Cloudflare Pro Through Tremhost From $9 Per Month

For SaaS businesses looking to explore additional Cloudflare website protection capabilities, Tremhost offers a Cloudflare Pro-based option from $9 per month.

This gives businesses another option when evaluating security and performance features for suitable public-facing websites and applications.

Visit Tremhost’s Cloudflare services page to review the available offering and determine whether it fits your application.

Before purchasing, confirm the included features, the number of websites covered and whether configuration assistance or ongoing management is part of the selected service. If your platform uses multiple subdomains, APIs or complex application infrastructure, clarify the intended coverage before making changes.

Businesses that require broader help with website and infrastructure risks can also explore Tremhost’s managed cybersecurity services.

The right security arrangement should reflect the application’s real requirements rather than rely on assumptions about what a single product can protect.

Build a More Resilient Foundation for Your SaaS Product

Customers expect SaaS applications to be accessible, dependable and appropriately protected. Meeting those expectations requires attention to application security, infrastructure reliability, access controls and ongoing maintenance.

Cloudflare Pro can help businesses manage certain web threats and improve the delivery of eligible content when configured appropriately. It should be considered as one component of a broader security strategy that protects the application and the systems supporting it.

If your business operates a public-facing SaaS website or compatible web application, explore Tremhost’s Cloudflare services to assess the available options from $9 per month.

Protecting the customer experience begins with understanding what your application needs, implementing suitable controls and maintaining those controls as the product grows.

How to Stop Malicious Bots From Targeting Your Business Website

0

Your business website can receive visitors at any hour of the day, from potential customers browsing your services to search engines discovering your latest content. But not every visitor is human, and not every automated request is harmless.

Some bots perform useful tasks, such as indexing public pages for search engines. Others repeatedly submit forms, scan websites for vulnerabilities, scrape information or generate traffic that places unnecessary pressure on the hosting environment. For businesses that rely on their websites to attract customers, distinguishing useful activity from unwanted traffic is an important part of maintaining a reliable online presence.

The difficulty is that malicious activity is not always obvious. A website may continue loading normally while receiving suspicious requests in the background. In other cases, excessive automated traffic can contribute to slow responses, unwanted form submissions or increased server resource usage.

Fortunately, businesses can take practical steps to identify suspicious activity and reduce unnecessary exposure. Cloudflare Pro provides additional website security capabilities that can help manage certain malicious HTTP requests. Through Tremhost, businesses can explore Cloudflare Pro-based protection from $9 per month.

https://tremhost.com/cloudflare/

What Are Website Bots, and Why Do They Visit Your Website?

A bot is software that automatically performs tasks over the internet. Bots visit websites for many different reasons, and their presence does not automatically indicate a security problem.

Search engines use crawlers to discover public pages and understand website content. Monitoring tools may check whether a website is available, while legitimate services may collect information with permission. These activities can support the operation and visibility of a website.

Other bots have less helpful purposes. They may repeatedly request pages to collect publicly available information, submit spam through contact forms, test login pages or search for vulnerable software. Some automated requests may be part of broader attempts to exploit websites or disrupt their availability.

For a business website, the impact depends on the volume, behaviour and purpose of the requests. A small amount of unwanted traffic may have little noticeable effect, while repeated requests against resource-intensive pages can contribute to performance problems.

The objective should not be to eliminate every bot. Blocking legitimate search engine crawlers could interfere with how customers discover your website. Instead, businesses need appropriate controls that distinguish useful automated activity from requests that present a genuine problem.

Signs That Unwanted Bots May Be Affecting Your Website

One possible warning sign is a sudden increase in requests that does not correspond with an advertising campaign, seasonal promotion or other expected source of traffic. Server logs and available analytics may reveal repeated requests from particular sources or unusual patterns against specific URLs.

Another sign is a growing number of irrelevant contact form submissions. If your business receives repeated messages containing meaningless text, suspicious links or fabricated contact information, automated submissions may be contributing to the problem.

Repeated login attempts can also deserve investigation, particularly when they target administrator accounts or other sensitive areas. Similarly, a website that experiences unexpected increases in resource consumption may need its traffic patterns and application behaviour examined.

However, none of these signs proves that a malicious bot is responsible. Genuine visitors, software errors, search engine crawlers and other automated services can produce unusual patterns too.

Businesses should examine logs, request patterns and security events before applying restrictions. Understanding what is happening makes it easier to choose appropriate controls without blocking legitimate customers.

How Malicious Bots Can Affect Business Performance

Unwanted automated traffic can create several problems depending on the website and its hosting environment.

Repeated requests may consume server resources, particularly when they trigger database searches, account lookups or other resource-intensive application operations. If the website has limited capacity, excessive requests may contribute to slow responses for legitimate visitors.

Automated form submissions can also create unnecessary administrative work. Staff may need to review irrelevant messages, clean up records or distinguish genuine enquiries from spam. For a business that depends on its website to generate leads, this can reduce the efficiency of its customer acquisition process.

Some bots also scan websites for known vulnerabilities. If they discover outdated software or an exposed application component, the website may face further attempts to exploit that weakness.

It is important to distinguish unwanted traffic from a distributed denial-of-service attack. A DDoS attack is intended to overwhelm a target with traffic or requests from multiple sources. Ordinary bot activity does not necessarily constitute a DDoS attack, and each situation requires an appropriate response.

The first step is to determine whether the problem involves spam, excessive requests, vulnerability scanning, resource limitations or a more serious attack.

Practical Ways to Reduce Malicious Bot Traffic

Businesses can begin by reviewing how their websites handle automated requests. Contact forms should use appropriate validation and anti-spam controls, while login areas should be protected with strong passwords, multi-factor authentication where available and suitable rate limits.

Software maintenance is equally important. Keeping content management systems, themes and plugins updated helps address known vulnerabilities that automated scanners may attempt to exploit. Removing unused components and limiting administrative access can further reduce the website’s exposure.

Website owners should also review server logs and monitoring data to identify recurring patterns. If a particular endpoint is receiving excessive requests, the application may need additional controls or optimisation.

Where a traffic-management or security service is used, its rules should be configured carefully. Overly restrictive settings can block legitimate visitors, interfere with contact forms or disrupt important application functions.

These measures work best as part of a broader security strategy. No single technique can identify or stop every type of unwanted automated activity.

How Cloudflare Pro Can Help Manage Malicious Website Traffic

Cloudflare can sit between visitors and a website’s origin server when the relevant DNS records are configured and proxied correctly. This allows supported HTTP requests to pass through Cloudflare’s network before reaching the hosting environment.

Cloudflare Pro includes additional web application firewall capabilities that can help detect and block certain malicious requests. Depending on the available rules and configuration, these protections can help reduce exposure to some common web-based threats.

Cloudflare also provides DDoS protection for supported traffic, helping mitigate certain attacks intended to overwhelm online services. Its network can additionally deliver eligible cached content, which may reduce repeated requests to the origin server and improve delivery performance.

These capabilities can be valuable for businesses that need more options for managing unwanted web traffic. However, Cloudflare Pro does not automatically block every malicious bot, eliminate all spam or repair vulnerabilities in the underlying application.

Some unwanted requests may resemble legitimate activity, while certain attacks require application-level controls or changes to the hosting environment. Businesses should review available security events, test rule behaviour and investigate persistent problems rather than assuming that activating a service is sufficient.

The aim is to apply appropriate protection while keeping the website accessible to genuine customers and legitimate search engine crawlers.

Why Configuration Matters as Much as the Security Product

Purchasing a security service is only one part of protecting a website. The configuration determines how traffic is handled and which requests are allowed, challenged or blocked.

For Cloudflare to inspect the relevant web traffic, the appropriate DNS records must be configured for proxying. If a website uses multiple subdomains, administrators should review each relevant hostname rather than assume that protecting the homepage automatically covers every application.

The origin server also needs attention. If it accepts direct web connections that bypass the intended Cloudflare protection layer, additional controls may be necessary. Suitable origin firewall restrictions can help, but they must be implemented carefully to avoid disrupting legitimate services or administrative access.

Businesses should test important website functions after configuration changes. Login pages, enquiry forms, booking systems and checkout processes must continue to work as intended.

If suspicious activity persists, reviewing logs and security events can help determine whether the issue involves a configuration gap, an application vulnerability or a limitation that requires a different solution.

Get Cloudflare Pro Through Tremhost From $9 Per Month

Businesses that want to explore additional Cloudflare website security capabilities can consider Tremhost’s Cloudflare offering from $9 per month.

This provides an accessible option for businesses evaluating Cloudflare Pro without starting with a large technology budget. The appropriate service depends on the website’s requirements, the features needed and the level of assistance required.

Visit Tremhost’s Cloudflare services page to review the available options and determine whether they fit your website.

Before purchasing, confirm the included features, the number of websites covered and whether setup assistance or ongoing management is part of the selected service.

For businesses that need broader help with website and infrastructure risks, Tremhost’s managed cybersecurity services provide another starting point for evaluating additional support.

Cloudflare Pro should be treated as one layer of protection rather than a complete replacement for secure application development, software updates, reliable hosting and ongoing monitoring.

Protect Your Website Without Blocking Genuine Customers

Automated traffic is a normal part of operating a public website, but some requests can create unnecessary risks and operational problems. The right response depends on understanding the traffic, identifying the underlying issue and applying controls that match the website’s requirements.

Start by monitoring unusual requests, securing login areas, maintaining updated software and protecting forms against unwanted submissions. Investigate persistent performance problems and ensure that the hosting environment can support the website’s needs.

Cloudflare Pro can provide additional web application security capabilities and help manage certain unwanted traffic when configured appropriately. It is not a guarantee against every bot or attack, but it can contribute to a more comprehensive website protection strategy.

Tremhost offers Cloudflare Pro-based protection from $9 per month. Visit Tremhost’s Cloudflare services page to explore the available options.

Your website should be working to attract customers, not forcing your team to spend unnecessary time dealing with unwanted traffic.

Can Website Security Affect Your Google Rankings? What Business Owners Need to Know

0

Imagine spending months building your website’s visibility on Google. You have published useful content, optimised your pages and started attracting visitors who are interested in your products or services. Then, without warning, your website is compromised, visitors encounter security warnings, or your pages become unavailable.

The consequences can extend beyond the immediate technical problem. Potential customers may lose confidence in your business, search engines may struggle to access your pages, and the traffic you worked hard to earn could be affected.

This is why website security deserves a place in every serious SEO strategy. Search engine optimisation is not only about keywords, backlinks and content. Your website also needs to remain accessible, trustworthy and technically sound so that visitors and search engines can use it effectively.

Cloudflare Pro can contribute to that effort by providing additional website security and performance capabilities. Through Tremhost, businesses can explore Cloudflare Pro-based protection from $9 per month.

However, it is important to understand the relationship correctly. Cloudflare Pro does not automatically improve Google rankings, and installing it does not guarantee better search visibility. Its value lies in helping businesses address certain security and traffic risks that could otherwise interfere with their online presence.

https://tremhost.com/cloudflare/
Does Website Security Directly Affect Google Rankings?

Google uses many signals and systems to determine which pages appear in search results. Security is relevant to the overall health of a website, but there is no single security product that automatically moves a website higher in the rankings.

A properly secured website does not receive a guaranteed ranking boost simply because it uses Cloudflare Pro. Similarly, a website does not automatically lose all its rankings because it lacks a particular security subscription.

The more important issue is what happens when security problems affect the website itself.

If attackers compromise a website and inject malicious content, create unwanted pages or redirect visitors to harmful destinations, the website may develop problems that affect its search presence and reputation. Google may display warnings for sites it identifies as dangerous, and users may be discouraged from visiting them.

Technical disruptions can also make pages temporarily unavailable to search engine crawlers. If Google repeatedly encounters server errors or cannot access important content, it may affect how those pages are crawled and indexed over time.

These situations are different from a website simply not having a paid security service. Businesses should focus on preventing compromises, maintaining availability and resolving technical issues quickly rather than treating any security product as a ranking shortcut.

How a Hacked Website Can Damage Your Search Visibility

A compromised website can create problems that are difficult to notice immediately.

Attackers may insert hidden links, publish spam pages, alter existing content or redirect visitors to unrelated websites. In some cases, the changes may not be obvious when the business owner visits the homepage. The affected content could appear only on particular URLs or under specific conditions.

These changes can undermine the quality and trustworthiness of the website. They may also create unwanted pages that appear in search results or trigger security warnings for visitors.

For a business that depends on organic traffic, discovering a compromise late can make recovery more complicated. The website owner may need to identify the entry point, remove malicious content, update vulnerable software, restore trustworthy files and review the affected pages.

Simply activating Cloudflare does not clean a compromised website. If malware is already present, the business needs to investigate and remediate the incident rather than assuming that traffic protection has removed the underlying problem.

The best approach is to combine preventive security measures with monitoring, reliable backups and a recovery process that allows the business to respond quickly when something goes wrong.

Can Website Downtime Affect SEO?

Website downtime can interfere with the way customers and search engines access your content. The impact depends on the duration of the outage, how frequently it occurs, which pages are affected and how search engines encounter the problem.

A brief interruption does not necessarily cause a lasting ranking decline. However, extended or repeated availability problems can prevent crawlers from accessing pages and create a poor experience for visitors.

Imagine a business whose website becomes unavailable whenever traffic increases. Customers following links from Google may encounter errors instead of useful information. If the problem persists, the business risks losing enquiries while search engines may struggle to access its content consistently.

Downtime can have several causes, including hosting failures, application errors, database problems, network interruptions and malicious traffic. Identifying the actual cause is essential because different problems require different solutions.

Cloudflare can help manage supported web traffic and mitigate certain DDoS attacks, but it cannot guarantee that a website will remain online if the origin server fails or the application stops working.

Businesses should therefore review their hosting environment, monitor availability and investigate recurring server errors. Cloudflare can be part of a broader resilience strategy, but reliable infrastructure remains essential.

How Website Performance Fits Into the Picture

Visitors who arrive from Google expect a website to load and respond properly. If important pages take too long to display, users may abandon the experience before finding the information they need.

Google also considers page experience and performance-related signals in its ranking systems, although good performance alone cannot guarantee strong rankings. Relevant content, search intent, competition and many other factors remain important.

A content delivery network can help improve the delivery of eligible website resources. Cloudflare can cache suitable files, such as images, stylesheets and other static content, and serve them through its distributed network. Depending on the website’s configuration and the location of visitors, this may reduce latency and repeated requests to the origin server.

Cloudflare Pro includes additional plan-specific security and performance capabilities, but the actual performance benefit depends on the website. A slow database query, oversized image, inefficient script or underpowered hosting server may still require separate optimisation.

Businesses should measure performance before and after making changes rather than assume that purchasing a security service will automatically improve every page.

How Cloudflare Pro Can Help Protect Your Online Presence

Cloudflare operates as an intermediary between website visitors and the origin server when the relevant DNS records are configured and proxied correctly. This provides an opportunity to apply supported security and traffic-management features before requests reach the hosting environment.

Cloudflare Pro includes additional web application firewall capabilities that can help detect and block certain malicious HTTP requests. These controls can be useful for websites exposed to automated attacks and attempts to exploit application vulnerabilities, depending on the configuration and the traffic involved.

Cloudflare also provides DDoS protection for supported traffic. This can help mitigate attacks designed to overwhelm online services, reducing one potential source of disruption.

These capabilities matter to SEO because maintaining a secure, accessible website helps protect the content, customer experience and reputation on which organic traffic depends. They do not directly guarantee higher rankings, but they can contribute to a more resilient website.

Businesses should also remember that the security layer is only one part of the system. WordPress installations, plugins, themes, administrator accounts, databases and origin servers still need appropriate protection and maintenance.

For a wider view of how to check your setup, read Tremhost’s guide, Is Cloudflare Actually Protecting Your Website?.

Why Small Businesses Should Take Website Security Seriously

Small businesses sometimes assume that attackers are interested only in large companies. In reality, automated systems can scan websites at scale, without requiring an attacker to select each business individually.

A small company website may still contain outdated software, weak administrator credentials or publicly exposed services. If a vulnerability is exploitable, the business’s size does not automatically make the website safe.

The impact of a security incident can also be significant for a smaller organisation. A business that depends on Google traffic for enquiries may have fewer alternative channels to replace lost visitors. A compromised website can consume time, disrupt operations and create unexpected recovery expenses.

This does not mean every small business needs the most expensive security arrangement. It means the business should assess its exposure, keep software updated, use strong authentication, maintain backups and choose protection that matches its requirements.

Cloudflare’s Free plan provides useful foundational capabilities, while Pro adds further features for businesses that need them. The right choice depends on the website’s functionality, risk profile and technical requirements.

Get Cloudflare Pro Through Tremhost From $9 Per Month

Businesses looking to strengthen their website security can explore Cloudflare Pro-based protection through Tremhost from $9 per month.

The offering provides an accessible option for businesses evaluating additional Cloudflare security and performance capabilities without starting with a large technology budget.

Visit Tremhost’s Cloudflare services page to review the available options and determine whether they fit your website’s requirements.

Before purchasing, confirm the included features, website coverage and whether configuration assistance or ongoing management is part of the selected service. The value of a security service depends on more than the product itself; correct implementation and appropriate maintenance are important too.

Businesses that need help addressing wider website and infrastructure risks can also explore Tremhost’s managed cybersecurity services.

Cloudflare Pro should not be purchased solely in the expectation of a Google ranking boost. It should be considered when its additional protection and performance capabilities are appropriate for the website and the business risks involved.

Protect the Website Behind Your Google Traffic

Search visibility takes time and effort to build. Publishing useful content, earning relevant links and improving the user experience can all contribute to a stronger online presence. Protecting the website that supports those efforts is equally important.

Security problems can lead to malicious content, browser warnings, disrupted access and expensive recovery work. Performance and availability problems can also interfere with the experience customers and search engines expect.

Start by keeping your software updated, maintaining tested backups, reviewing access controls and monitoring important pages. Investigate unusual behaviour promptly and make sure your hosting environment can support the website’s needs.

Cloudflare Pro can add useful security and performance capabilities when configured appropriately, but it should be part of a broader strategy rather than treated as a shortcut to higher rankings.

Tremhost offers Cloudflare Pro-based protection from $9 per month. Visit Tremhost’s Cloudflare services page to explore the available options.

Your Google rankings depend on many factors. Protecting the website behind them helps you safeguard the online presence your business has worked to build.