Home Blog Page 31

Do You Need a WAF If You Already Have Antivirus and a Firewall on Your Server?

0

This is one of the most common — and most reasonable — points of confusion in website security: “I already have a firewall and antivirus on my server, isn’t that enough?” It’s a fair question, because the terms get used loosely, and the honest answer is that these tools protect against genuinely different things. Neither replaces the other.

What a Server Firewall Actually Does

A traditional firewall — the kind built into your server or provided at the network level — controls traffic based on things like IP addresses, ports, and protocols. Think of it as deciding who is allowed to knock on which doors of your server. It’s very good at blocking obviously unwanted connections: traffic on ports that shouldn’t be open, connections from IP ranges you’ve blocked, protocols you don’t use.

What it’s not built to do is look inside a legitimate-looking web request and evaluate whether the actual content of that request is malicious. A firewall generally can’t tell the difference between a normal login attempt and a SQL injection attempt sent to the same login form on the same port — because from the firewall’s perspective, both are just “allowed traffic on port 443.”

What Antivirus Actually Does

Server-side antivirus scans files on your server for known malicious code — malware signatures, suspicious file patterns, known exploit kits. This matters, but it’s fundamentally reactive and file-based: it’s looking for bad things that are already on your server, not evaluating incoming web traffic as it happens in real time.

What a WAF Actually Does (And Why It’s Different)

A Web Application Firewall operates at a completely different layer: it inspects the actual content of HTTP/HTTPS requests — form submissions, URL parameters, headers — as they arrive, and evaluates whether that content matches known attack patterns before it ever reaches your application. This is what catches things like:

  • SQL injection attempts hidden inside a form field
  • Cross-site scripting (XSS) payloads in a comment or search box
  • Malicious file upload attempts disguised as normal uploads
  • Application-specific abuse, like repeated password-guessing on a login form that technically looks like “normal” traffic to a network firewall

The key distinction: a network firewall looks at where traffic is coming from and which door it’s using; a WAF looks at what the traffic is actually saying once it’s already through the door.

Why You Genuinely Need Both, Not Either/Or

Layer What It Catches What It Misses
Network firewall Unwanted connections by IP/port/protocol Malicious content inside allowed traffic
Antivirus Known malware already on the server Real-time malicious web requests
WAF Malicious content within legitimate-looking web requests Non-web-based server intrusions

None of these three fully covers what the others do. A site with a solid network firewall and clean antivirus scans can still be compromised through its contact form, login page, or checkout process — because those are exactly the paths a WAF is built to inspect and the other two aren’t designed to look at.

A Concrete Example

Imagine a WordPress login page. A network firewall allows traffic on port 443 because that’s normal web traffic — it has no way to distinguish a real user logging in from a script attempting hundreds of password combinations, because both look identical at the network level. Antivirus isn’t involved at all, since no file is being uploaded or executed. A WAF, however, can recognize the pattern — repeated POST requests to the same login endpoint at a mechanical rate — and apply rate limiting specifically to that behavior, which is precisely what neither of the other two tools is positioned to do.

Where This Fits Into Tremhost Armor

This is exactly why Armor Lite includes baseline firewall rules covering bad bots, XML-RPC abuse, and login endpoint protection even at the entry tier because these are web-application-layer risks, not network-layer ones. Armor Pro extends this with a full managed WAF ruleset tuned to your specific application, plus rate limiting on the endpoints that matter most, like login and checkout the exact gap a server-level firewall and antivirus were never built to close.

The Honest Bottom Line

Antivirus and a server firewall aren’t wasted effort they matter for different threats. But if your site accepts any kind of user input a login form, a contact form, a checkout page, a comment section a WAF isn’t a redundant extra layer on top of what you already have. It’s covering ground those other tools structurally can’t reach.

How Cloudflare Stops DDoS Attacks Before They Reach Your Server

0

In today’s digital economy, website downtime is more than an inconvenience—it can mean lost revenue, damaged customer trust, and missed business opportunities. Whether you operate an online store, a corporate website, a school portal, or a WordPress blog, your website is constantly exposed to cyber threats. Among the most dangerous of these threats are Distributed Denial-of-Service (DDoS) attacks, which are designed to overwhelm your website with malicious traffic until it becomes inaccessible.

Traditional hosting providers are built to serve legitimate visitors, not absorb billions of malicious requests generated by global botnets. This is why businesses around the world rely on Cloudflare, one of the world’s largest cybersecurity and content delivery networks, to protect their websites from DDoS attacks before they ever reach the hosting server.

At Tremhost, we’ve taken this protection a step further through Tremhost Armor, our fully managed Cloudflare security service. Instead of expecting business owners to configure complex firewall rules and security settings themselves, Tremhost Armor delivers professionally managed protection that keeps websites secure, fast, and online around the clock.

Understanding Why Traditional Servers Struggle During DDoS Attacks

Every website has a finite amount of computing power, memory, network bandwidth, and processing capacity. Under normal circumstances, these resources are more than enough to serve legitimate visitors.

During a DDoS attack, however, attackers use thousands or even millions of compromised devices across the internet to flood a website with fake traffic. Instead of receiving a few hundred visitors, the server may suddenly receive millions of requests every minute.

Without protection, the hosting server must attempt to process every incoming request. Eventually, its resources become exhausted, causing slow performance, timeout errors, or complete downtime.

This is why many businesses discover that simply having a powerful hosting plan is not enough. Even the fastest servers can become overwhelmed if malicious traffic reaches them directly.

Cloudflare Acts as a Protective Shield

One of Cloudflare’s greatest strengths is that it sits between your visitors and your website.

Rather than allowing internet users to connect directly to your hosting server, Cloudflare becomes the first point of contact. Every visitor first reaches Cloudflare’s global network, where each request is inspected before it is allowed to continue to your website.

Think of Cloudflare as a highly trained security team stationed at the entrance to your business. Every visitor is screened before entering. Genuine customers are welcomed in immediately, while suspicious individuals are stopped before they ever reach your premises.

Because malicious traffic is filtered at Cloudflare’s network edge, your hosting server only receives legitimate requests.

A Global Network Built to Absorb Massive Attacks

Cloudflare operates one of the largest and most advanced global networks in the world, with hundreds of data centers strategically positioned across multiple continents.

Instead of relying on a single location to process traffic, Cloudflare distributes incoming requests across its worldwide infrastructure.

This global capacity is what makes Cloudflare exceptionally effective against DDoS attacks. Even attacks generating terabits of traffic can be distributed across the network, preventing any single server or data center from becoming overwhelmed.

For attackers, this presents an enormous challenge. Instead of attacking one server, they are effectively attacking an entire global security platform specifically engineered to withstand these assaults.

Intelligent Traffic Analysis in Real Time

Not every surge in website traffic is malicious.

A successful marketing campaign, viral social media post, or breaking news story can all generate legitimate spikes in visitors.

Cloudflare uses advanced behavioral analysis and machine learning to distinguish between genuine users and malicious bots.

Rather than simply counting requests, Cloudflare examines factors such as request patterns, browser behavior, network reputation, geographic distribution, protocol anomalies, and known attack signatures.

This intelligent analysis allows real visitors to continue browsing your website while malicious requests are identified and blocked almost instantly.

Automatic DDoS Detection and Mitigation

One of the biggest advantages of Cloudflare is its ability to respond automatically.

Traditional security systems often require administrators to manually identify attacks before implementing defensive measures. During that delay, significant damage may already have occurred.

Cloudflare continuously monitors global traffic patterns twenty-four hours a day. When suspicious behavior is detected, automated mitigation systems activate immediately without requiring human intervention.

Attack traffic is filtered, suspicious connections are challenged or blocked, and legitimate visitors continue accessing the website with minimal disruption.

This rapid response dramatically reduces downtime and helps businesses maintain uninterrupted online services.

Protecting Against Different Types of DDoS Attacks

Modern DDoS attacks vary significantly in both size and technique.

Some attacks focus on consuming internet bandwidth through enormous traffic floods. Others exploit weaknesses within networking protocols, while more sophisticated attacks repeatedly request login pages, search functions, shopping carts, or API endpoints until web applications become overloaded.

Cloudflare is designed to defend against each of these attack categories through a combination of network filtering, protocol validation, application-layer analysis, and intelligent traffic management.

This multi-layered approach provides comprehensive protection against evolving attack methods.

Hiding Your Origin Server from Attackers

Many cybercriminals attempt to bypass security services by discovering the actual IP address of the hosting server.

If attackers can identify your origin server, they may launch attacks directly against it.

Cloudflare helps prevent this by acting as a reverse proxy. Visitors interact with Cloudflare instead of your hosting server, keeping your origin IP address hidden from public view.

Within Tremhost Armor, this protection is professionally configured to ensure your infrastructure remains concealed while legitimate traffic continues flowing securely through Cloudflare.

Reducing exposure in this way significantly limits opportunities for attackers to target your hosting environment directly.

Rate Limiting Prevents Abuse

Not every cyberattack involves massive traffic volumes.

Some attackers repeatedly attempt to log in to administrator accounts, abuse search forms, overwhelm checkout pages, or flood APIs with automated requests.

Cloudflare’s rate limiting technology identifies excessive activity from individual IP addresses and automatically slows or blocks abusive behavior.

For businesses using Tremhost Armor Pro and Business, these rate-limiting policies are professionally configured to protect sensitive areas of the website without interrupting normal customer activity.

This additional layer of protection is especially valuable for WordPress websites, WooCommerce stores, membership platforms, and customer portals.

Tremhost Armor Makes Cloudflare Easy

Although Cloudflare offers powerful security tools, many businesses struggle to configure them correctly.

Improper firewall rules may accidentally block legitimate visitors. Incorrect SSL settings can generate browser security warnings. Poor cache configuration may cause outdated website content to appear.

Tremhost Armor removes these challenges by providing fully managed Cloudflare configuration and optimization.

Our specialists handle DNS migration, SSL installation, origin certificates, firewall deployment, caching optimization, bot protection, security tuning, and ongoing maintenance.

Rather than learning complex networking concepts, businesses receive enterprise-grade security that simply works.

Emergency Protection When Your Website Is Already Under Attack

Unfortunately, many organizations only seek cybersecurity assistance after their website has already gone offline.

For these situations, Tremhost Armor SOS provides rapid emergency response.

Our engineers quickly migrate your DNS to Cloudflare, activate Under Attack Mode, deploy emergency firewall rules, configure aggressive rate limiting, rotate compromised origin IP addresses where necessary, and stabilize your website as quickly as possible.

Once the attack has been contained, we provide a detailed incident summary explaining what happened, what was blocked, and what security improvements have been implemented to reduce future risk.

This service helps businesses recover quickly while strengthening their long-term security posture.

Why Businesses Trust Tremhost Armor

Cloudflare is one of the most respected cybersecurity platforms in the world, protecting millions of websites every day. However, its effectiveness depends heavily on proper configuration and ongoing management.

Tremhost Armor combines Cloudflare’s world-class infrastructure with Tremhost’s expertise in website hosting, cybersecurity, and performance optimization.

Businesses benefit from enterprise-grade DDoS mitigation, managed firewall protection, intelligent caching, secure DNS management, performance improvements, and expert technical support—all delivered as a fully managed service.

Instead of worrying about cyber threats, you can focus on growing your business while Tremhost ensures your website remains secure, available, and performing at its best.

Final Thoughts

Cyberattacks continue to grow in both frequency and sophistication, but website owners are no longer powerless. Modern cybersecurity is about stopping threats before they ever reach your infrastructure, and that’s exactly what Cloudflare was designed to do.

By filtering malicious traffic across its global network, hiding your origin server, automatically mitigating attacks, and intelligently distinguishing between legitimate visitors and cybercriminals, Cloudflare provides one of the strongest defenses available today.

With Tremhost Armor, you don’t just gain access to Cloudflare—you gain a team of experts who configure, manage, and optimize your protection from day one.

Whether you’re running a personal website, an online business, or a mission-critical enterprise platform, proactive security is one of the smartest investments you can make. The best time to prepare for a DDoS attack is long before one ever happens.

Armor Lite vs. Pro vs. Business: Which Tremhost Security Tier Actually Fits Your Site?

0

“Which plan do I need?” is a fair question to ask before committing to anything, and most pricing pages don’t actually answer it — they just list features and expect you to self-sort. Here’s a direct comparison of Tremhost Armor Lite, Pro, and Business, organized around the actual question that matters: what kind of site do you run, and what’s actually at risk if something goes wrong?

The Three Tiers, Side by Side

Feature Armor Lite Armor Pro Armor Business
Price $35/month ($30 setup) $3,540/year See plan details
DNS/CNAME setup Included Included Included
Universal SSL, Full (Strict) Included Included Included
Proxy (hides origin IP) Included Included Included
Baseline firewall (bad bots, XML-RPC, login endpoints) Included Included Included
Unmetered DDoS protection Included Included Included
Full managed WAF ruleset, false-positive tuned — Included Included
Custom WAF rules for your application — Included Expanded capacity
Rate limiting on login/checkout — Included Included
Image optimization — Included Included
Automatic Platform Optimization (WordPress) — Included Included
Monthly security & traffic report — Included Included
PCI DSS-ready configuration guidance — — Included
Prioritized support escalation — — Included
Quarterly configuration review — — Included

Armor Lite: The Baseline Everyone Should Have

Who it’s for: a personal site, a small brochure-style business site, a blog, or any site where the main risk is “basic bad traffic” rather than a targeted, sustained attack.

Lite covers the fundamentals that genuinely matter for almost any website: your origin IP is hidden, SSL is properly configured rather than left on a weaker default, and baseline rules catch the most common abuse patterns — bad bots, XML-RPC abuse, login endpoint probing. Unmetered DDoS protection means there’s no volume ceiling where the protection itself becomes the bottleneck.

What it doesn’t cover: anything requiring custom tuning for your specific application, rate limiting on sensitive endpoints like checkout, or ongoing visibility into what’s actually being attempted against your site.

Armor Pro: For Sites With Something to Actually Protect

Who it’s for: an active WordPress site, an online store, a membership site, or anything where login abuse, checkout fraud, or application-specific vulnerabilities are realistic risks — not just generic bot noise.

The jump from Lite to Pro is really the jump from “generic protection” to “protection tuned to your actual site.” A managed WAF ruleset tuned to avoid false positives means legitimate traffic doesn’t get blocked by accident — a common frustration with poorly configured firewalls. Custom WAF rules mean the protection reflects what your specific application actually does, not a one-size-fits-all template. Rate limiting on login and checkout endpoints directly addresses the two places most abuse concentrates. And the monthly report means you’re not just hoping it’s working — you can actually see what was blocked.

What it doesn’t cover: compliance-specific configuration or the kind of ongoing human review that comes with Business tier.

Armor Business: For Sites Handling Real Stakes

Who it’s for: ecommerce businesses processing payments, sites with regulatory or compliance obligations, or any business where downtime or a breach has a serious financial or reputational cost — and where “we’ll get to it” isn’t an acceptable response time.

Business tier isn’t just “more rules” — it’s expanded custom rule capacity for more complex applications, PCI DSS-ready configuration guidance for businesses handling payment data, prioritized support escalation (meaning you’re not in a general queue when something’s wrong), and quarterly configuration reviews, which matter because security configuration isn’t a “set once” task — what was correctly configured six months ago may not reflect how your site or traffic has changed since.

Worth being honest about: if you’re not handling payment data directly and don’t have compliance requirements, Business tier’s specific additions (PCI guidance, quarterly reviews) may be more than you actually need — Pro may be the better fit even for a fairly active site.

A Simple Way to Decide

Ask these in order:

  1. Does your site handle payment data directly, or have compliance requirements? → Business
  2. Does your site have logins, checkout, or a specific application worth protecting beyond basic hosting? → Pro
  3. Do you just need solid, unmetered baseline protection with your origin IP hidden? → Lite

What Happens If You Guess Wrong

Moving between tiers isn’t a one-way decision — a site that starts on Lite and grows into needing custom rules or rate limiting can move to Pro later, and the reverse is also reasonable if a Business-tier feature set turns out to be more than what’s actually needed. The honest approach is starting with what your site’s current risk profile calls for, not the most expensive tier “just in case.”

What Is a DDoS Attack and How Can You Stop One?

0

Every second, thousands of websites around the world are targeted by cyberattacks. Some attacks are designed to steal sensitive information, while others aim for something much simpler but equally damaging: making your website unavailable to legitimate visitors. One of the most common and disruptive forms of cyberattack is the Distributed Denial-of-Service (DDoS) attack.

Whether you run an online store, a corporate website, a school portal, a government platform, or a personal blog, a DDoS attack can interrupt your services, damage your reputation, and cost your business thousands of dollars in lost revenue. As businesses become increasingly dependent on their online presence, understanding DDoS attacks has become essential for every website owner.

Fortunately, modern security solutions such as Tremhost Armor, powered by Cloudflare, provide enterprise-grade DDoS protection that keeps websites online even during large-scale attacks.

Understanding a DDoS Attack

A Distributed Denial-of-Service (DDoS) attack occurs when thousands—or even millions—of internet-connected devices simultaneously send enormous amounts of traffic to a website or online service.

Unlike normal website traffic generated by real users, DDoS traffic is malicious. The goal is not to browse your website or make a purchase but to overwhelm your server with requests until it can no longer respond. When this happens, legitimate visitors experience slow loading times, connection errors, or complete website outages.

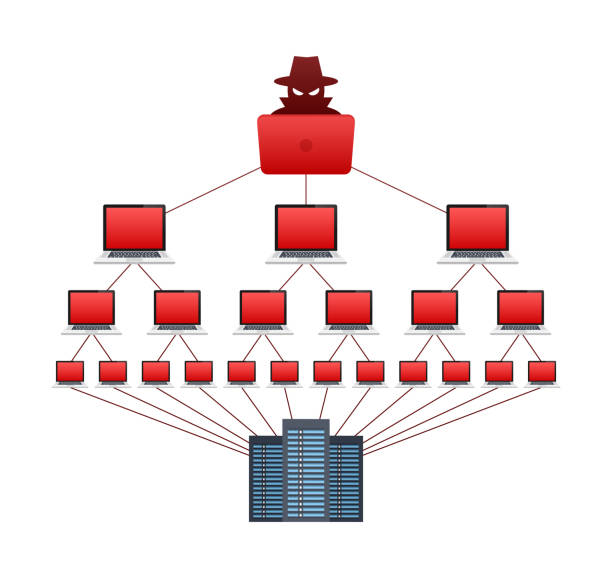
The word “distributed” is important because the attack originates from many different devices located across the world rather than from a single computer. These devices often belong to a botnet, a network of computers, servers, or Internet of Things (IoT) devices that have been infected with malware and secretly controlled by cybercriminals.

Because attacks come from thousands of different locations simultaneously, blocking them manually becomes extremely difficult without specialized protection.

How DDoS Attacks Work

Imagine owning a small restaurant with seating for fifty customers. On a normal day, genuine customers walk in, order food, and enjoy their meals.

Now imagine thousands of people suddenly enter the restaurant—not because they want to eat, but simply to occupy every available seat and block the entrance. Real customers cannot get inside, your staff cannot serve anyone, and your business effectively stops operating.

This is exactly what happens during a DDoS attack.

Instead of filling chairs, attackers flood your web server with fake requests until its resources—such as CPU power, memory, bandwidth, or network connections—are exhausted. Once those resources are consumed, your website becomes unavailable to legitimate users.

Why Cybercriminals Launch DDoS Attacks

There are many reasons attackers perform DDoS attacks, and not all of them involve large corporations.

Some attackers seek financial gain by demanding payment to stop the attack. Others attempt to disrupt competitors, while some launch attacks simply for notoriety or as part of larger hacking campaigns.

Online retailers may be attacked during major sales events to interrupt business operations. Educational institutions often experience attacks during examination periods. Government agencies may become targets for political reasons, while gaming platforms frequently face attacks from disgruntled players.

Regardless of the motivation, the outcome is usually the same: downtime, frustrated users, and financial losses.

The Different Types of DDoS Attacks

Modern DDoS attacks come in several forms, each targeting different parts of your infrastructure.

Volumetric attacks attempt to consume all available internet bandwidth by generating enormous amounts of traffic. These attacks are among the largest ever recorded and can involve terabits of malicious data every second.

Protocol attacks focus on exhausting server resources by exploiting weaknesses in networking protocols. Even websites with significant bandwidth can become unavailable if their servers are overwhelmed by protocol-based attacks.

Application-layer attacks target the website itself rather than the network. Instead of flooding servers with meaningless traffic, attackers repeatedly request pages, search functions, login portals, or shopping carts until the web application becomes overloaded. These attacks are particularly dangerous because they often resemble legitimate user behavior.

Effective protection requires defenses against all three attack types.

Warning Signs That Your Website May Be Under Attack

Many business owners initially assume their hosting provider is experiencing technical difficulties when, in reality, their website is under active attack.

One of the first warning signs is an unexpected slowdown in website performance. Pages that normally load within seconds suddenly become sluggish or fail entirely.

You may also notice frequent timeout errors, unusually high server resource usage, or spikes in bandwidth consumption. Visitors might report receiving “503 Service Unavailable” or “Connection Timed Out” messages, while your hosting dashboard may indicate abnormal traffic levels.

If these symptoms appear suddenly without a corresponding increase in genuine visitors, a DDoS attack may be occurring.

The Business Impact of Website Downtime

Website downtime affects far more than technical performance.

For eCommerce businesses, every minute of downtime means lost sales and abandoned shopping carts. Service-based companies lose inquiries and customer trust, while news websites, educational institutions, and nonprofit organizations may be unable to serve their audiences during critical periods.

Beyond immediate financial losses, repeated outages can damage your brand’s reputation. Customers expect websites to be available whenever they need them. If your website frequently becomes inaccessible, many visitors will simply choose a competitor instead.

Search engines also monitor website availability. Prolonged downtime may reduce search engine visibility, impacting your long-term digital marketing efforts.

Why Traditional Hosting Alone Is Not Enough

Many people assume their hosting provider automatically protects them against every cyberattack.

While quality hosting providers maintain secure infrastructure, most hosting servers are not designed to absorb the enormous traffic volumes generated during modern DDoS attacks.

If malicious traffic reaches your server directly, it must compete with legitimate users for the same resources. Eventually, even powerful servers can become overwhelmed.

This is why dedicated DDoS mitigation services have become an essential layer of website security.

How Tremhost Armor Stops DDoS Attacks

Tremhost Armor uses Cloudflare’s globally distributed network to intercept malicious traffic before it reaches your website.

Instead of connecting directly to your hosting server, visitors first connect to Cloudflare’s edge network, which spans hundreds of data centers worldwide.

Every incoming request is analyzed in real time. Intelligent systems identify suspicious behavior, malicious bots, abnormal traffic patterns, and known attack signatures. Harmful traffic is blocked immediately, while legitimate visitors continue accessing your website without interruption.

Because attacks are absorbed across Cloudflare’s massive global infrastructure, your origin server remains protected even during extremely large-scale attacks.

This proactive approach ensures that your business remains online while attackers waste their resources against Cloudflare’s protective network rather than your website.

Additional Layers of Protection

DDoS protection is only one part of a comprehensive security strategy.

Tremhost Armor also provides professionally configured SSL certificates, secure DNS management, origin IP protection, managed Web Application Firewall (WAF) rules, rate limiting, intelligent caching, and performance optimization.

Together, these technologies create multiple layers of defense that significantly reduce your website’s exposure to cyber threats while improving loading speed and reliability.

Instead of relying on a single security feature, Tremhost Armor delivers comprehensive protection that adapts to modern attack techniques.

Emergency Protection When Every Minute Counts

Sometimes attacks begin without warning.

For businesses already experiencing an active cyberattack, Tremhost Armor SOS provides rapid emergency response.

Our team performs an accelerated DNS cutover to Cloudflare, enables Under Attack Mode, deploys emergency firewall rules, implements aggressive rate limiting, rotates compromised origin IP addresses when necessary, and delivers a detailed post-incident report explaining exactly what occurred.

This rapid response minimizes downtime and helps businesses recover quickly while strengthening their defenses against future attacks.

Don’t Wait Until Your Website Goes Offline

The unfortunate reality is that every website connected to the internet is constantly being scanned by automated bots looking for vulnerabilities. It is no longer a question of if your website will be targeted, but when.

Investing in DDoS protection before an attack occurs is significantly less expensive than recovering from prolonged downtime, lost sales, damaged customer confidence, and emergency technical work.

With Tremhost Armor powered by Cloudflare, businesses gain enterprise-grade DDoS protection, professional security management, and the confidence that their websites remain available even when cybercriminals attempt to bring them down.

Your website is one of your business’s most valuable assets. Protect it before attackers have the opportunity to exploit it.

The Complete Guide to Website Security: How Tremhost Armor Powered by Cloudflare Protects Your Business

0

In today’s digital world, your website is more than just an online presence—it’s your storefront, marketing engine, customer support center, and often your primary source of revenue. Whether you run an eCommerce store, a corporate website, a WordPress blog, or a business portal, your website is constantly exposed to cyber threats. Every day, millions of websites face attacks ranging from distributed denial-of-service (DDoS) attacks and malicious bots to SQL injection attempts, brute-force login attacks, and sophisticated malware campaigns.

Unfortunately, many businesses only realize the importance of website security after experiencing an attack. Downtime, data breaches, lost customer trust, declining search engine rankings, and unexpected recovery costs can be devastating. Preventing these incidents is far less expensive than recovering from them.

This is where Tremhost Armor, powered by Cloudflare, comes in. Designed to provide enterprise-grade protection for businesses of all sizes, Tremhost Armor combines Cloudflare’s world-renowned global security network with Tremhost’s expert management and support. The result is a comprehensive managed website security solution that protects your website while improving speed, reliability, and overall performance.

Why Website Security Matters More Than Ever

Cybercrime has evolved into one of the largest global industries, targeting organizations of every size. Contrary to popular belief, hackers don’t only target multinational corporations. Small businesses, startups, bloggers, educational institutions, nonprofits, and local businesses are often easier targets because they typically have fewer security measures in place.

A successful cyberattack can lead to website downtime, stolen customer information, ransomware infections, blacklisting by search engines, and permanent damage to your brand’s reputation. Even a few hours of downtime during peak business hours can translate into significant financial losses.

Search engines like Google also prioritize secure websites. Websites that experience repeated security issues or extended downtime can lose valuable rankings, reducing organic traffic and making it harder for potential customers to find your business online. Website security is no longer just an IT concern—it is a business necessity and an important part of your digital marketing strategy.

What Is Tremhost Armor?

Tremhost Armor is a fully managed Cloudflare security service designed to protect websites from modern cyber threats while improving website speed and reliability.

Unlike simply creating a Cloudflare account and enabling basic protection, Tremhost Armor is professionally configured, monitored, and optimized by security specialists who understand how to maximize Cloudflare’s powerful features for different types of websites.

Whether you operate a WordPress website, WooCommerce store, corporate portal, educational platform, or custom web application, Tremhost Armor provides tailored protection that fits your specific requirements.

Powered by Cloudflare’s Global Security Network

Cloudflare operates one of the world’s largest content delivery and cybersecurity networks, with hundreds of data centers strategically located across the globe. Every visitor to your website connects to the nearest Cloudflare edge location before traffic reaches your web server.

This architecture provides multiple advantages simultaneously. It filters malicious traffic, blocks attacks before they reach your server, caches website content for faster loading, reduces server resource usage, and helps maintain availability even during massive traffic spikes.

By combining Cloudflare’s infrastructure with Tremhost’s managed service, businesses receive enterprise-level protection without needing in-house cybersecurity expertise.

Advanced DDoS Protection for Modern Businesses

Distributed Denial-of-Service (DDoS) attacks remain one of the most common methods attackers use to overwhelm websites with enormous amounts of fake traffic.

Without proper protection, a DDoS attack can make your website unavailable for hours or even days. Customers cannot access your services, online stores stop processing orders, and search engine crawlers may interpret prolonged downtime as a sign of an unreliable website.

Tremhost Armor leverages Cloudflare’s unmetered DDoS protection to identify and absorb malicious traffic before it reaches your hosting server. Because attacks are stopped at Cloudflare’s global network, your origin server remains protected while legitimate visitors continue accessing your website normally.

This proactive defense ensures your business stays online when it matters most.

Enterprise-Grade Web Application Firewall (WAF)

Modern cyberattacks rarely rely on brute force alone. Many attackers attempt to exploit vulnerabilities in websites through techniques such as SQL injection, cross-site scripting (XSS), remote code execution, and malicious bot traffic.

The Web Application Firewall (WAF) included with Tremhost Armor continuously analyzes incoming requests and blocks malicious behavior before attackers can exploit vulnerabilities.

For businesses using Tremhost Armor Pro and Business plans, custom firewall rules can also be configured to match the unique behavior of your applications, reducing false positives while maximizing protection.

This intelligent firewall works around the clock without affecting the experience of legitimate users.

Hide Your Origin Server and Strengthen Infrastructure Security

One of the most overlooked aspects of website security is protecting the origin server itself.

Without a reverse proxy, attackers can often discover your server’s IP address and launch attacks directly against your infrastructure.

Tremhost Armor enables Cloudflare’s proxy service, ensuring your origin IP remains hidden from public view. This significantly reduces the attack surface and prevents many common attack techniques from reaching your hosting environment.

Combined with secure DNS management and Full (Strict) SSL configuration, your infrastructure becomes substantially more resilient against external threats.

Optimized Website Performance Alongside Strong Security

Many business owners assume that stronger security means slower website performance. In reality, properly configured security can actually improve loading speeds.

Tremhost Armor optimizes Cloudflare’s global caching, image delivery, browser caching, and content distribution to accelerate your website for visitors worldwide.

For WordPress websites, Tremhost Armor Pro includes Automatic Platform Optimization (APO), allowing pages to be served directly from Cloudflare’s global edge network. This dramatically reduces page load times, decreases server load, and improves user experience.

Faster websites not only create happier visitors but also contribute to improved search engine rankings and higher conversion rates.

Professional Cloudflare Configuration Without the Complexity

Cloudflare offers hundreds of configuration options, and incorrect settings can accidentally break websites, interfere with applications, or leave security gaps.

Many businesses struggle with questions such as:

Should proxy mode be enabled?

How should SSL certificates be configured?

What cache rules should be used?

How should login pages be protected?

Which firewall rules are actually necessary?

Tremhost Armor removes this complexity by handling every aspect of Cloudflare configuration professionally.

Our engineers perform DNS migration, SSL implementation, origin certificate installation, firewall optimization, caching configuration, rate limiting, and ongoing adjustments so you don’t have to.

Flexible Protection for Every Business

Tremhost Armor offers multiple service tiers to accommodate businesses at different stages of growth.

Tremhost Armor Lite provides essential website security with DNS migration, Cloudflare proxy protection, Full (Strict) SSL configuration, optimized caching, firewall setup, and unmetered DDoS protection. It is ideal for small businesses, blogs, portfolios, and startup websites seeking reliable protection.

Tremhost Armor Pro expands on this foundation with managed WAF rules, custom firewall policies, rate limiting, image optimization, Automatic Platform Optimization for WordPress, and detailed monthly security reports. This plan is well suited for growing businesses, online stores, and websites handling significant customer traffic.

Tremhost Armor Business delivers advanced Cloudflare Business-tier protection with expanded firewall capabilities, PCI DSS-ready configuration guidance, prioritized support escalation, and regular security reviews. It is designed for organizations where uptime, compliance, and performance are mission-critical.

For businesses experiencing an active cyberattack, Tremhost Armor SOS provides emergency protection through rapid DNS migration, Under Attack Mode activation, emergency firewall deployment, origin IP rotation if compromised, and a detailed post-incident report explaining what happened and how the issue was resolved.

Website Security That Supports SEO

Search engine optimization extends beyond keywords and backlinks. Google rewards websites that provide a secure, reliable, and fast experience.

Secure HTTPS connections, improved Core Web Vitals, reduced downtime, faster page loading, and consistent website availability all contribute positively to search engine visibility.

By reducing security incidents and optimizing performance simultaneously, Tremhost Armor supports the technical SEO foundation every successful website needs.

Why Businesses Choose Tremhost Armor

Many organizations begin using Cloudflare independently but quickly discover that effective security requires far more than enabling a few settings.

Tremhost Armor combines industry-leading Cloudflare technology with experienced engineers who understand website security, performance optimization, and ongoing maintenance. Instead of spending hours learning firewall rules, DNS records, SSL certificates, and caching strategies, businesses can focus on growth while Tremhost manages the technical complexity.

This managed approach reduces risk, minimizes downtime, and provides peace of mind that your website is protected by experts.

Secure Your Website Before Attackers Find It

Cybersecurity is no longer optional. Every website connected to the internet is continuously scanned by automated bots looking for vulnerabilities to exploit. Waiting until after an attack occurs often leads to unnecessary downtime, lost revenue, damaged customer trust, and costly recovery efforts.

Tremhost Armor empowers businesses with enterprise-grade Cloudflare security that is professionally configured, continuously optimized, and backed by expert support. Whether you need essential protection for a small business website or advanced security for a mission-critical application, Tremhost Armor delivers the confidence to operate online without compromising security or performance.

Your website is one of your most valuable business assets. Protect it with a solution designed to defend against today’s threats while preparing for tomorrow’s challenges.
How Much Does Emergency Website Security Cost? A Transparent Pricing Guide

0

When a site is actively under attack, the last thing anyone wants is to call around getting vague quotes before getting help. Pricing for emergency security support is often buried behind “contact us” forms precisely because providers don’t want to commit to a number upfront. Here’s a transparent, actual-numbers breakdown — what emergency response costs, what ongoing protection costs, and how the two relate.

Emergency Response: The One-Time Cost

Tremhost Armor SOS: $150.00, one-time.

This covers the full emergency response — same-day DNS cutover to Cloudflare, Under Attack Mode activation, custom emergency WAF and rate-limiting rules, origin IP rotation if your server’s real address has been exposed, and a post-incident summary once things are stable.

There’s no hidden tiering here — it’s a flat, one-time fee for stabilizing an active incident, not a subscription and not a variable quote based on “severity.”

Why This Number Matters More Than It Looks

To put $150 in context: the cost of downtime for a business relying on its website for sales, bookings, or leads can exceed that within a single hour, depending on the business. This isn’t meant as a scare tactic — it’s simply the actual math worth doing before deciding whether “wait and see” or “call for help now” is the more expensive option.

Ongoing Protection: The Monthly/Annual Cost

Emergency response solves the immediate problem. It doesn’t replace ongoing protection, which is priced separately and works out considerably cheaper per month than a repeated emergency would cost:

Plan Price What’s Included
Armor Lite $35.00/month ($30 setup) DNS/CNAME setup, Universal SSL, proxy protection, baseline firewall rules, cache tuning, unmetered DDoS protection
Armor Pro $3,540.00/year Everything in Lite, plus full managed WAF, custom rules, rate limiting on login/checkout, image optimization, monthly security report
Armor Business $150.00 (see plan details for billing terms) Everything in Pro, plus Business-tier WAF, PCI DSS-ready configuration, prioritized support, quarterly reviews

The Honest Math: Emergency vs. Prevention

Here’s the comparison worth actually sitting with: Armor SOS costs $150 once, for a site that’s already in crisis. Armor Lite costs $35/month — meaning roughly four months of ongoing, proactive protection costs about the same as a single emergency response. The difference is that Lite is working continuously to prevent the emergency from happening at all, while SOS is a reactive fix after the fact.

Neither is “wrong” to choose — a site that’s never had an incident and has low risk exposure may reasonably run without paid protection for a while. But once a site has actually experienced an incident, the math shifts: the emergency has already demonstrated the cost of not having protection, and ongoing coverage at $35/month is the considerably cheaper path compared to the possibility of paying $150 again for the next one.

What Drives Cost Up (and What Doesn’t)

To be transparent about what’s not a hidden fee: Armor SOS is a flat $150 regardless of how complex the specific incident is — a straightforward DDoS versus a more involved compromise requiring origin IP rotation both fall under the same price. What does change the ongoing cost is which tier of continuous protection makes sense afterward, which depends on factors like whether you’re handling payment data directly (pointing toward Business) or just need solid baseline protection (Lite) or tuned application-specific rules (Pro).

A Simple Way to Decide

Your Situation Reasonable Starting Point
Site is under attack or compromised right now Armor SOS ($150 one-time)
No protection yet, want to prevent future incidents Armor Lite ($35/month)
Running an application with login/checkout worth protecting Armor Pro ($3,540/year)
Handling payment data, need compliance-ready configuration Armor Business

The Bottom Line

Emergency security support doesn’t have to be a mystery quote you’re afraid to ask about mid-crisis. $150 gets a full, same-day stabilization. From there, the real decision is whether the monthly cost of not needing that call again is worth it — for most businesses that have already had one incident, it is.

Cloudflare Under Attack Mode Explained: When to Use It and What It Actually Does

0

“Just turn on Under Attack Mode” is common advice during a website incident, but it’s rarely explained beyond that one sentence. Here’s what the setting actually does mechanically, when it genuinely helps, and — just as importantly — when it’s the wrong tool for what’s happening.

What Under Attack Mode Actually Does

When active, every visitor to your site is shown a brief interstitial page — usually for a few seconds — while their browser is checked to confirm it’s behaving like a real browser rather than an automated script. Only after passing this check does the visitor get through to your actual site content.

Mechanically, this works because real browsers can execute certain background checks (JavaScript challenges) the way a genuine browser would, while simple automated scripts used in attacks typically can’t, or don’t bother to. The check filters out a large share of unsophisticated automated traffic before it ever reaches your server, without requiring any manual identification of which requests are “bad.”

What This Is Actually Solving

Recall the core problem in most attacks: your server has finite capacity, and an attack works by exceeding that capacity with more requests than it can process. Under Attack Mode doesn’t make your server handle more traffic — it reduces the amount of illegitimate traffic that reaches your server at all, by filtering it out at the Cloudflare layer before it ever gets there. Fewer requests reaching the server means the server itself has a fighting chance of handling what’s left.

When to Actually Turn It On

  • Active DDoS traffic — your site is slow, timing out, or unreachable, and you suspect volume-based attack traffic rather than a genuine surge in real visitors
  • Known bot/scraping surges — a sudden flood of automated traffic hitting the site aggressively
  • During an active security incident — as part of broader containment while other fixes (WAF rules, credential resets) are being put in place

When It’s the Wrong Tool

This is the part usually left out of the advice. Under Attack Mode adds friction for every visitor, real or not — which means:

  • It’s not meant to run permanently. Leaving it on all the time adds unnecessary friction to every legitimate visitor, which can hurt conversion rates, frustrate returning customers, and in some cases affect how search engines crawl your site.
  • It won’t help with a genuine traffic surge from real visitors — like a viral moment or a big promotion — since the slowdown there isn’t from bots, it’s from real demand. Under Attack Mode won’t distinguish “attack” from “unusually popular,” so this scenario needs different handling (caching, scaling), not this setting.
  • It doesn’t fix a compromised site — if the issue is malware, defacement, or unauthorized access rather than traffic volume, Under Attack Mode does nothing to address the actual breach; it’s a traffic-layer tool, not a cleanup tool.

What It Looks Like From a Visitor’s Perspective

A real visitor sees a short-lived checking page — typically a matter of seconds — before being let through automatically. It’s mildly noticeable but not usually disruptive for a one-time visit during a known, temporary incident. The trade-off only becomes a real problem if it’s left running long after the emergency has actually passed.

How This Fits Into a Broader Response

Under Attack Mode is rarely the only thing that should happen during an incident — it’s one piece alongside custom WAF rules targeting the specific attack pattern, rate limiting on sensitive endpoints like login or checkout, and, if the origin IP may be exposed, rotating it so attackers can’t simply bypass Cloudflare entirely and hit the server directly. Turning on Under Attack Mode alone, without addressing an exposed origin IP, can create a false sense of security — the front door is filtered, but a side door might still be open.

Where This Fits in Tremhost’s Services

Scenario What Applies
No Cloudflare/proxy set up yet, active attack right now Armor SOS — same-day cutover + Under Attack Mode activation
Cloudflare already active, want ongoing tuned protection Armor Pro — managed WAF, custom rules, rate limiting
Need to toggle Under Attack Mode occasionally yourself Available directly if you’re already on any Armor tier

The Short Version

Under Attack Mode is a temporary, blunt-but-effective filter for suspected bot and attack traffic — genuinely useful in the right moment, actively counterproductive if left on indefinitely, and not a substitute for addressing the actual cause of an incident once things are stable.

The Ultimate Guide to Website Security in 2026 | Protect Your Business from Modern Cyber Threats

0

A business website has become far more than a digital brochure. It is often the first point of contact for customers, the center of online sales, a communication platform, and a repository of valuable customer information. Whether you operate a small local business, a growing e-commerce store, or a multinational enterprise, your website plays a critical role in your success.

Unfortunately, cybercriminals understand this just as well as business owners do.

Every day, millions of automated attacks scan the internet searching for vulnerable websites. These attacks are no longer limited to large corporations. In fact, many hackers intentionally target small and medium-sized businesses because they often lack dedicated cybersecurity teams and advanced protection.

Website security is no longer optional. It has become a fundamental business requirement.

In 2026, cyber threats continue to evolve rapidly. Artificial intelligence is helping businesses improve efficiency, but it is also enabling attackers to automate phishing campaigns, identify vulnerabilities faster, and launch more sophisticated attacks. Businesses that rely solely on basic hosting security or outdated plugins are exposing themselves to unnecessary risks.

This comprehensive guide explains everything business owners need to know about website security, the threats facing modern websites, and the practical steps every organization should take to protect its digital assets.

What Is Website Security?

Website security refers to the collection of technologies, policies, and best practices designed to protect websites, servers, applications, and users from cyber threats.

The objective is simple: keep your website available, your customer information safe, and your business operating without interruption.

Website security extends far beyond installing an SSL certificate or using a strong password. It involves multiple layers of protection working together to defend against different types of attacks.

Some of these protective measures include:

  • Secure hosting infrastructure
  • Firewalls
  • SSL/TLS encryption
  • Malware detection
  • DDoS mitigation
  • Secure DNS management
  • Regular software updates
  • Access control
  • Backup systems
  • Continuous monitoring

Think of website security as protecting a modern office building.

A security guard alone is not enough.

You also need locked doors, surveillance cameras, alarm systems, visitor management, fire protection, emergency exits, and regular maintenance.

Your website works exactly the same way.

Every security layer reduces the likelihood of a successful attack.

Website Security Is a Continuous Process

One of the biggest misconceptions is that website security is something you “set up once.”

Cybersecurity doesn’t work that way.

Hackers constantly develop new attack techniques. Software vendors release security patches every week. New vulnerabilities are discovered almost daily.

Protecting a website requires continuous monitoring, regular updates, and proactive improvements.

Businesses that treat security as an ongoing investment recover faster from incidents and experience significantly less downtime.

Why Website Security Matters More Than Ever

Cybercrime has transformed dramatically over the last decade.

Previously, attacks required technical expertise.

Today, hacking tools can be purchased or rented online, making sophisticated attacks accessible even to inexperienced criminals.

Automated bots now scan millions of websites around the clock looking for:

  • Weak passwords
  • Outdated software
  • Vulnerable plugins
  • Misconfigured servers
  • Exposed databases
  • Poor DNS settings

Once a weakness is identified, attacks can begin within minutes.

The result may include:

  • Website downtime
  • Stolen customer information
  • SEO penalties
  • Lost revenue
  • Damaged reputation
  • Legal consequences
  • Ransom demands

Businesses that underestimate these risks often discover the true cost only after an attack has already occurred.

Website Security by the Numbers

The following table highlights why cybersecurity has become a business priority.

Security Reality Why It Matters
Cyber attacks occur every day worldwide Every website is a potential target.
Most attacks are automated Hackers don’t need to know your business personally.
Small businesses are frequently targeted Limited security often makes them easier to compromise.
Website downtime reduces customer trust Visitors may never return after a poor experience.
Data breaches can lead to financial losses Recovery often costs significantly more than prevention.

These realities demonstrate that every organization—regardless of size—needs a security strategy.

The Growing Cost of Cybercrime

For many businesses, the financial consequences of a cyberattack extend far beyond repairing a hacked website.

The true costs often include:

  • Lost online sales
  • Customer compensation
  • Emergency technical support
  • Reputation management
  • SEO recovery
  • Regulatory penalties
  • Legal expenses
  • Increased insurance costs

Imagine an online store that generates thousands of dollars every day.

If the website becomes unavailable during a major promotion, every hour of downtime represents lost revenue.

Even after services are restored, rebuilding customer confidence may take months.

For service-based businesses, downtime can mean missed enquiries, cancelled appointments, and reduced customer confidence.

Website security should therefore be viewed as business continuity rather than merely an IT expense.

Common Website Security Threats in 2026

Cyber threats continue evolving as technology advances.

Understanding the most common attack methods helps businesses make informed security decisions.

Distributed Denial-of-Service (DDoS) Attacks

A DDoS attack overwhelms a website with enormous volumes of malicious traffic.

The objective is to consume server resources until legitimate visitors can no longer access the website.

Large attacks may involve millions of compromised devices spread across multiple countries.

Without proper protection, websites can become inaccessible within minutes.

Fortunately, modern DDoS mitigation platforms can identify malicious traffic and block it before it reaches the origin server.

Malware Infections

Malware refers to malicious software designed to damage websites, steal information, redirect visitors, or provide attackers with unauthorized access.

Malware may:

  • Redirect visitors to scam websites
  • Display unwanted advertisements
  • Steal login credentials
  • Encrypt website files
  • Install hidden backdoors

Many website owners remain unaware of infections until search engines begin warning visitors.

Brute Force Attacks

Brute force attacks repeatedly attempt thousands—or even millions—of username and password combinations until successful.

WordPress login pages are particularly common targets.

Without rate limiting, strong passwords, and additional authentication controls, these attacks may eventually succeed.

SQL Injection

SQL Injection attacks exploit poorly secured database queries.

Successful attacks can allow criminals to:

  • View confidential information
  • Modify records
  • Delete databases
  • Create administrator accounts

Proper coding standards and firewall protection significantly reduce this risk.

Cross-Site Scripting (XSS)

Cross-Site Scripting allows attackers to inject malicious scripts into legitimate webpages.

Victims may unknowingly reveal sensitive information or perform actions while logged into trusted websites.

Modern Web Application Firewalls (WAFs) help detect and block these attacks before they reach applications.

Bot Attacks

Not all website traffic comes from real people.

Malicious bots continuously scan websites looking for weaknesses.

Common bot activities include:

  • Credential stuffing
  • Price scraping
  • Content theft
  • Spam submissions
  • Fake account creation
  • Resource exhaustion

Intelligent bot management solutions distinguish legitimate users from malicious automation.

Comparing Common Website Threats

Threat Primary Goal Business Impact Recommended Protection
DDoS Attack Downtime Lost revenue DDoS Protection
Malware Data theft or disruption Reputation damage Malware scanning & WAF
Brute Force Account compromise Unauthorized access Rate limiting & MFA
SQL Injection Database access Data breach Secure coding & WAF
XSS User compromise Customer trust issues WAF & secure development
Bot Attacks Abuse & automation Performance loss Bot management

Why Small Businesses Are Prime Targets

One of the biggest myths in cybersecurity is that hackers only target large enterprises.

The reality is very different.

Small businesses are often considered easier targets because they typically have fewer security resources, smaller IT teams, and limited monitoring capabilities.

Attackers understand that compromising hundreds of small websites can be just as profitable as attacking one large organization.

Many cybercriminals use automated tools that do not distinguish between a multinational corporation and a local family business.

If a vulnerability exists, the attack proceeds automatically.

This means every website connected to the internet should be considered a potential target.

The Business Impact of a Security Breach

A successful cyberattack affects far more than technology.

Customers lose confidence.

Employees lose productivity.

Search engine rankings decline.

Revenue decreases.

Recovery costs increase.

Businesses may spend weeks restoring systems, investigating incidents, communicating with customers, and repairing reputational damage.

By contrast, implementing proactive website security significantly reduces these risks while improving customer trust and operational resilience.

Website security is ultimately an investment in long-term business stability rather than simply a technical safeguard.

Built in Africa, Securing Globally: How Tremhost Handles Security Incidents Across Time Zones

0

A website attack has no relationship to the clock in your particular time zone. A DDoS attempt doesn’t wait for your support provider’s office to open; a brute-force script doesn’t check what time it is in the region where a company happens to be headquartered. This is a genuinely practical problem in emergency security support, and it’s worth talking about directly rather than glossing over with vague “24/7 support” language that most hosting marketing leans on without explanation.

The Real Problem With Single-Region Support

A lot of hosting and security providers are built around a single region’s business hours, with an “emergency” line that’s really just a queue that gets attention once the home office wakes up. For a business whose customers, traffic, and — most relevantly — attackers, aren’t confined to one time zone, that gap between “the incident started” and “someone competent is actually looking at it” can be the entire difference between a contained situation and a full outage.

This isn’t a knock on any specific provider — it’s just a structural reality of how a lot of hosting companies are built, growing from a local base and expanding support second.

Where Tremhost’s Footprint Actually Comes From

Tremhost’s positioning — “Built in Africa, trusted globally, Harare to Houston, Nairobi to NYC, London, Dubai, Singapore” — isn’t just a tagline for marketing copy. It reflects a genuinely distributed customer base and operational reality: sites and businesses spread across multiple continents, which means incidents don’t cluster conveniently into one region’s working hours. A brute-force attempt against a Nairobi-based ecommerce store and a DDoS attempt against a Houston-based SaaS product aren’t going to politely take turns during one office’s 9-to-5.

What This Means Practically for Emergency Response

Being built around a genuinely global customer base from the outset shapes how emergency response actually has to work — not as an add-on “we also cover other time zones” feature, but as a baseline assumption in how the service is structured. When an Armor SOS emergency comes in, the response isn’t dependent on which specific hour it happens to be in one particular headquarters city.

Why This Matters More for Emergencies Than Routine Support

For a routine support ticket — a billing question, a general how-to — a delay of a few hours is an inconvenience. For an active security incident, the same delay is a completely different category of problem: it’s the gap between an attack being caught in its early, containable stage versus discovered only after significant damage, downtime, or data exposure has already occurred.

This is really the core argument for why “emergency support” as a phrase needs to mean something specific and structural, rather than being a generic reassurance layered onto a support system built for a single region’s convenience.

Global Reach, Local Understanding

There’s a second, less obvious advantage to operating across this many regions: exposure to a genuinely wide range of hosting environments, attack patterns, and regional infrastructure quirks — from ISPs and connectivity conditions in different parts of the world, to the kinds of attack traffic that tend to originate from or target specific regions. A provider that’s only ever dealt with one region’s typical traffic patterns has a narrower frame of reference than one that’s regularly handling incidents across genuinely different environments.

What This Looks Like From the Customer Side

The practical takeaway, stated plainly: when something goes wrong with your site, the response isn’t gated behind “wait until it’s morning somewhere specific.” Whether the incident happens to align with business hours in Harare, London, or Singapore is not the deciding factor in whether your site gets emergency attention.

We Asked: What Does “Emergency Security Support” Actually Include? (A Transparent Breakdown of Tremhost Armor SOS)

0

“Emergency security support” is one of those phrases that shows up constantly in hosting marketing and rarely gets explained. It sounds reassuring, but if you’re the one actually deciding whether to pay for it — especially mid-crisis, when your site is already down — a vague promise isn’t good enough. So instead of another marketing summary, here’s a literal, line-by-line breakdown of what’s actually included in Tremhost Armor SOS, and why each piece exists.

Line Item 1: Emergency DNS Cutover to Cloudflare (Same-Day)

What this means in practice: if your site currently has no proxy protection at all — traffic going directly to your server with nothing filtering it — this is the process of routing your domain’s traffic through Cloudflare instead, on the same day the emergency is happening, rather than the multi-day timeline of a standard, unhurried migration.

Why it’s a distinct line item: a normal DNS/proxy setup is deliberately paced to avoid misconfiguration. Doing it safely and quickly, under pressure, while a site may already be struggling, is a different skill than doing it carefully over several days — which is why this isn’t just “the same service, faster.”

Line Item 2: Under Attack Mode Activation

What this means in practice: once traffic is routed through Cloudflare, this specific setting adds a brief automated verification step in front of every visitor before they reach your site — filtering out much of the automated, script-driven traffic typical of an active attack.

Why it’s a distinct line item: this isn’t switched on by default even with a standard Cloudflare setup, because it does add a small amount of friction for legitimate visitors — it’s a deliberate, situational trade-off made specifically when a site is actively under pressure, not a permanent setting.

Line Item 3: Emergency WAF and Rate-Limiting Rules

What this means in practice: rather than deploying generic, one-size-fits-all firewall rules, this is building rules specific to what’s actually happening to your site right now — if it’s a login brute-force, rate limiting goes directly on the login endpoint; if it’s XML-RPC abuse, that specific vector gets closed.

Why it’s a distinct line item: generic rule sets can miss the specific attack pattern happening in the moment, or worse, block legitimate traffic unnecessarily. Custom, situation-specific rules take deliberate configuration — this is diagnostic work, not a template being applied.

Line Item 4: Origin IP Rotation (If Compromised)

What this means in practice: if there’s reason to believe your server’s real IP address is already known to an attacker, this replaces it with a new one and ensures every path to your site goes through the proxy going forward — closing the direct route that would otherwise let attackers bypass all of the above protections entirely.

Why it’s a distinct line item: this step is only necessary when there’s evidence of exposure, but when it is needed, it’s the difference between protection that’s genuinely effective versus protection that looks complete on paper while a known bypass still exists.

Line Item 5: Post-Incident Summary

What this means in practice: a clear, written account of what happened and exactly what was changed — not a log dump, a readable summary covering the timeline, likely entry point, actions taken, and current status.

Why it’s a distinct line item: fixing a site and documenting what was fixed are two different deliverables. Without this, six months from now there’s no record to check against if something looks off again — and no clear account to give customers or auditors if one is needed.

What’s Deliberately Not Included (And Why That’s Honest, Not a Gap)

To be transparent about scope: Armor SOS is built to stabilize an active emergency, not to be ongoing protection. It doesn’t include continuous WAF tuning, monthly reporting, or quarterly reviews — those are what Armor Lite, Pro, and Business are for. Positioning a one-time emergency service as a replacement for ongoing protection would be misleading; it’s the fix for right now, not the plan for going forward.

The Full Picture in One Table

Included Purpose
Same-day DNS cutover Get traffic behind protection immediately
Under Attack Mode Filter automated attack traffic in real time
Emergency WAF/rate limiting Close the specific attack vector in use
Origin IP rotation Remove any existing bypass to your real server
Post-incident summary Document what happened and what changed

Price: $150.00, one-time.

When This Makes Sense vs. When It Doesn’t

Armor SOS makes sense if your site has no existing proxy or WAF protection and something is actively happening right now. If you already have Armor Lite or Pro running, most of this is already in place proactively — the emergency scenario this solves largely doesn’t arise in the first place, which is really the underlying point of having ongoing protection at all.