To set up a firewall on your server, install a host firewall such as UFW (Ubuntu and Debian) or firewalld (AlmaLinux, Rocky Linux and other Red Hat-based systems), deny incoming traffic by default, then allow only the ports your services need, starting with SSH. Allow SSH before you enable the firewall, or you can lock yourself out. This guide walks through both tools and the checks to make afterwards.
What a server firewall does
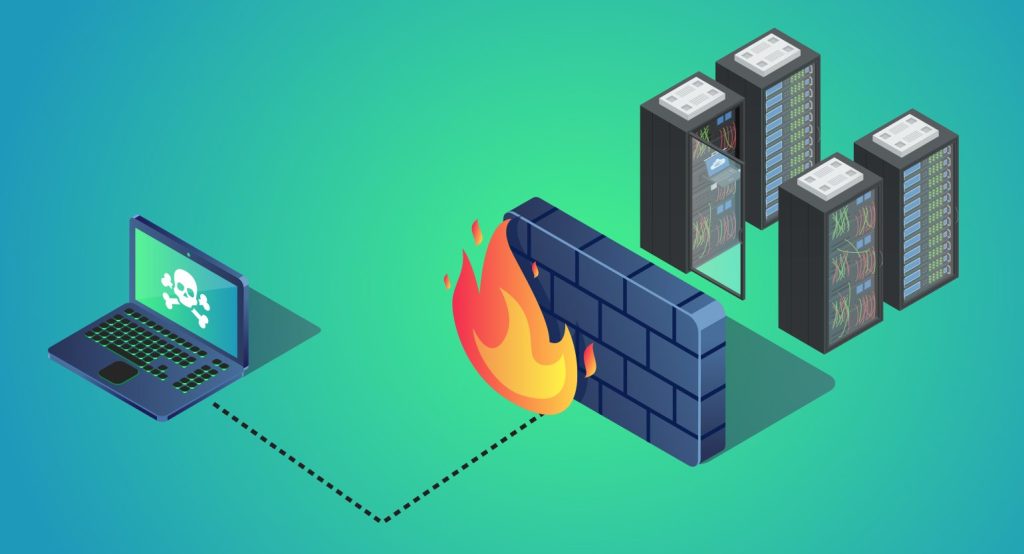
A firewall filters network traffic using rules. On a Linux server, the kernel’s netfilter system does the filtering, and tools such as UFW and firewalld give you a simpler way to write the rules. A sensible default policy is:
- Deny all incoming connections unless a rule allows them.
- Allow outgoing connections, so the server can install updates and send email.
- Allow only the ports you use, such as SSH on 22, HTTP on 80 and HTTPS on 443.
A firewall is one layer of protection. It does not replace updates, strong SSH keys or application security.
Before you start
- Log in as root or a user with sudo rights.
- Know which ports your services use. Check with sudo ss -tulpn, which lists listening ports and the programs behind them.
- Know your SSH port. If you changed it from 22, use your port number in the rules below.
- Have a way back in. Most VPS providers offer a web console that works even if SSH is blocked.
Option 1: UFW on Ubuntu or Debian
- Install UFW: sudo apt update then sudo apt install ufw.
- Set the defaults: sudo ufw default deny incoming and sudo ufw default allow outgoing.
- Allow SSH first: sudo ufw allow OpenSSH, or sudo ufw allow 22/tcp.
- Allow web traffic: sudo ufw allow 80/tcp and sudo ufw allow 443/tcp.
- Enable the firewall: sudo ufw enable.
- Check the rules: sudo ufw status verbose.
To slow down password-guessing attacks on SSH, replace the SSH rule with sudo ufw limit OpenSSH, which blocks addresses that open too many connections in a short time. To allow SSH only from your office IP, use sudo ufw allow from 203.0.113.10 to any port 22 proto tcp and remove the general SSH rule. Replace the example address with your own.
Option 2: firewalld on AlmaLinux or Rocky Linux
- Install and start firewalld: sudo dnf install firewalld then sudo systemctl enable –now firewalld.
- Allow SSH: sudo firewall-cmd –permanent –add-service=ssh.
- Allow web traffic: sudo firewall-cmd –permanent –add-service=http and sudo firewall-cmd –permanent –add-service=https.
- Apply the changes: sudo firewall-cmd –reload.
- Check the rules: sudo firewall-cmd –list-all.
The –permanent flag saves a rule so it survives a reboot, and –reload makes it active. To open a single port, use –add-port=8080/tcp in place of –add-service. firewalld groups rules into zones; most servers use the default public zone.
Ports you may need
Open only what the server actually runs. Common examples:
- 22 SSH.
- 80 and 443 websites over HTTP and HTTPS.
- 25, 465 and 587 sending email (SMTP).
- 993 and 995 receiving email over IMAP and POP3 with SSL.
- 53 TCP and UDP, only if the server is a DNS nameserver.
- 2083 and 2087 cPanel and WHM over SSL, on cPanel servers. Webmail uses 2096.
Never open database ports such as 3306 for MySQL to the whole internet. If a remote system needs database access, allow only that system’s IP address.
Firewalls on cPanel servers
cPanel servers need many ports open for web, email, FTP and the panels themselves. Use a firewall tool that your control panel and security software support, rather than adding raw rules that other software may overwrite. On Tremhost managed servers, Imunify360 provides a firewall alongside malware scanning. Check the vendor documentation before changing firewall software on a production cPanel server.
Common mistakes
- Enabling the firewall before allowing SSH. You lose access instantly.
- Running two firewall managers at once, such as UFW and firewalld. Their rules conflict. Use one.
- Forgetting Docker. Docker writes its own rules for published container ports, which can bypass UFW. Bind containers to 127.0.0.1 or follow Docker’s firewall guidance.
- Opening ports “just in case”. Every open port is something an attacker can probe.
- Not testing. From another machine, check that open ports respond and closed ports do not.
- Not checking after a reboot. Restart the server once after setup and confirm the firewall starts on its own and the rules are still there.
- Leaving old rules. When you remove a service, remove its firewall rule too. Review the rule list every few months.
Frequently asked questions
Is a firewall enough to secure a server?
No. Also keep the system updated, use SSH keys instead of passwords, disable root password login, and run malware scanning on servers that host websites.
Should I use UFW or firewalld?
Use the one that is standard for your distribution: UFW on Ubuntu and Debian, firewalld on AlmaLinux, Rocky Linux and other Red Hat-based systems.
Do I need a firewall on shared hosting?
No. On shared hosting the provider manages the server firewall. Server firewalls matter when you run your own VPS or dedicated server.
I locked myself out. What now?
Use your provider’s web console to log in, then add the SSH rule or disable the firewall with sudo ufw disable or sudo systemctl stop firewalld.
Next step
Tremhost KVM VPS plans give you full root access to set up your own firewall. If you would rather have the server secured and maintained for you, see Managed cPanel VPS or managed security.